 yuyr
59a38513a4
测试方案: - lm2机器端口映射到本机:18080, 18081, 8082-8085 - 访问URL: http://localhost:18080/dashboard 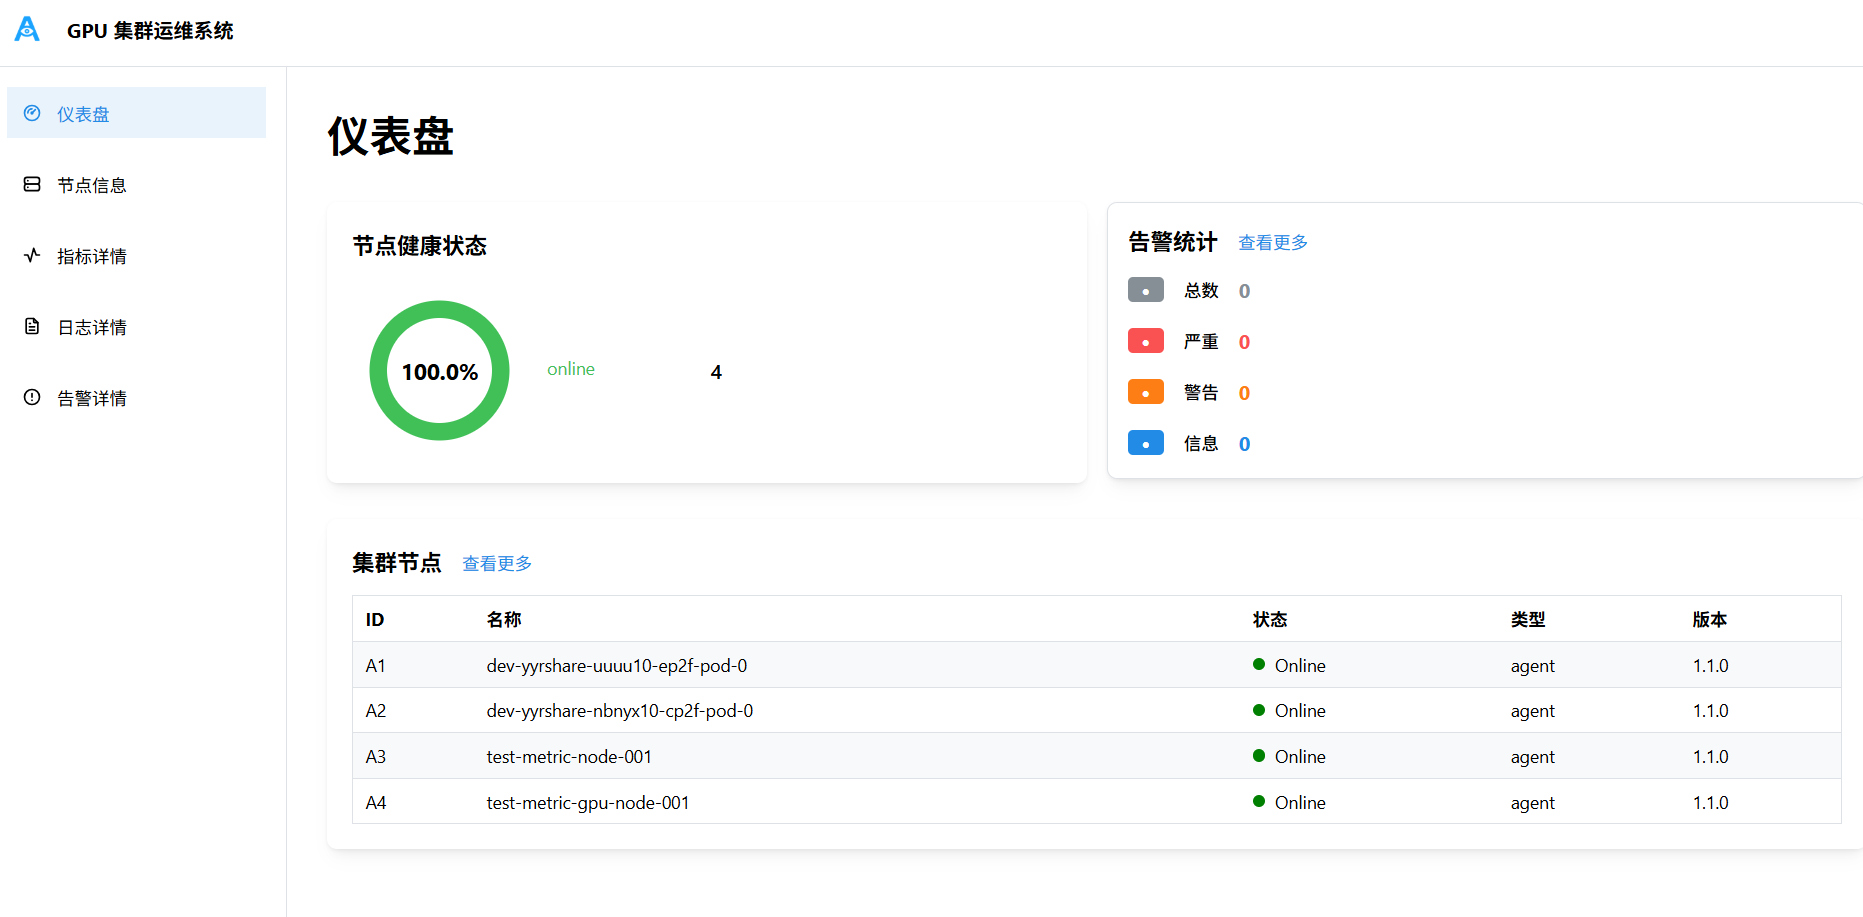 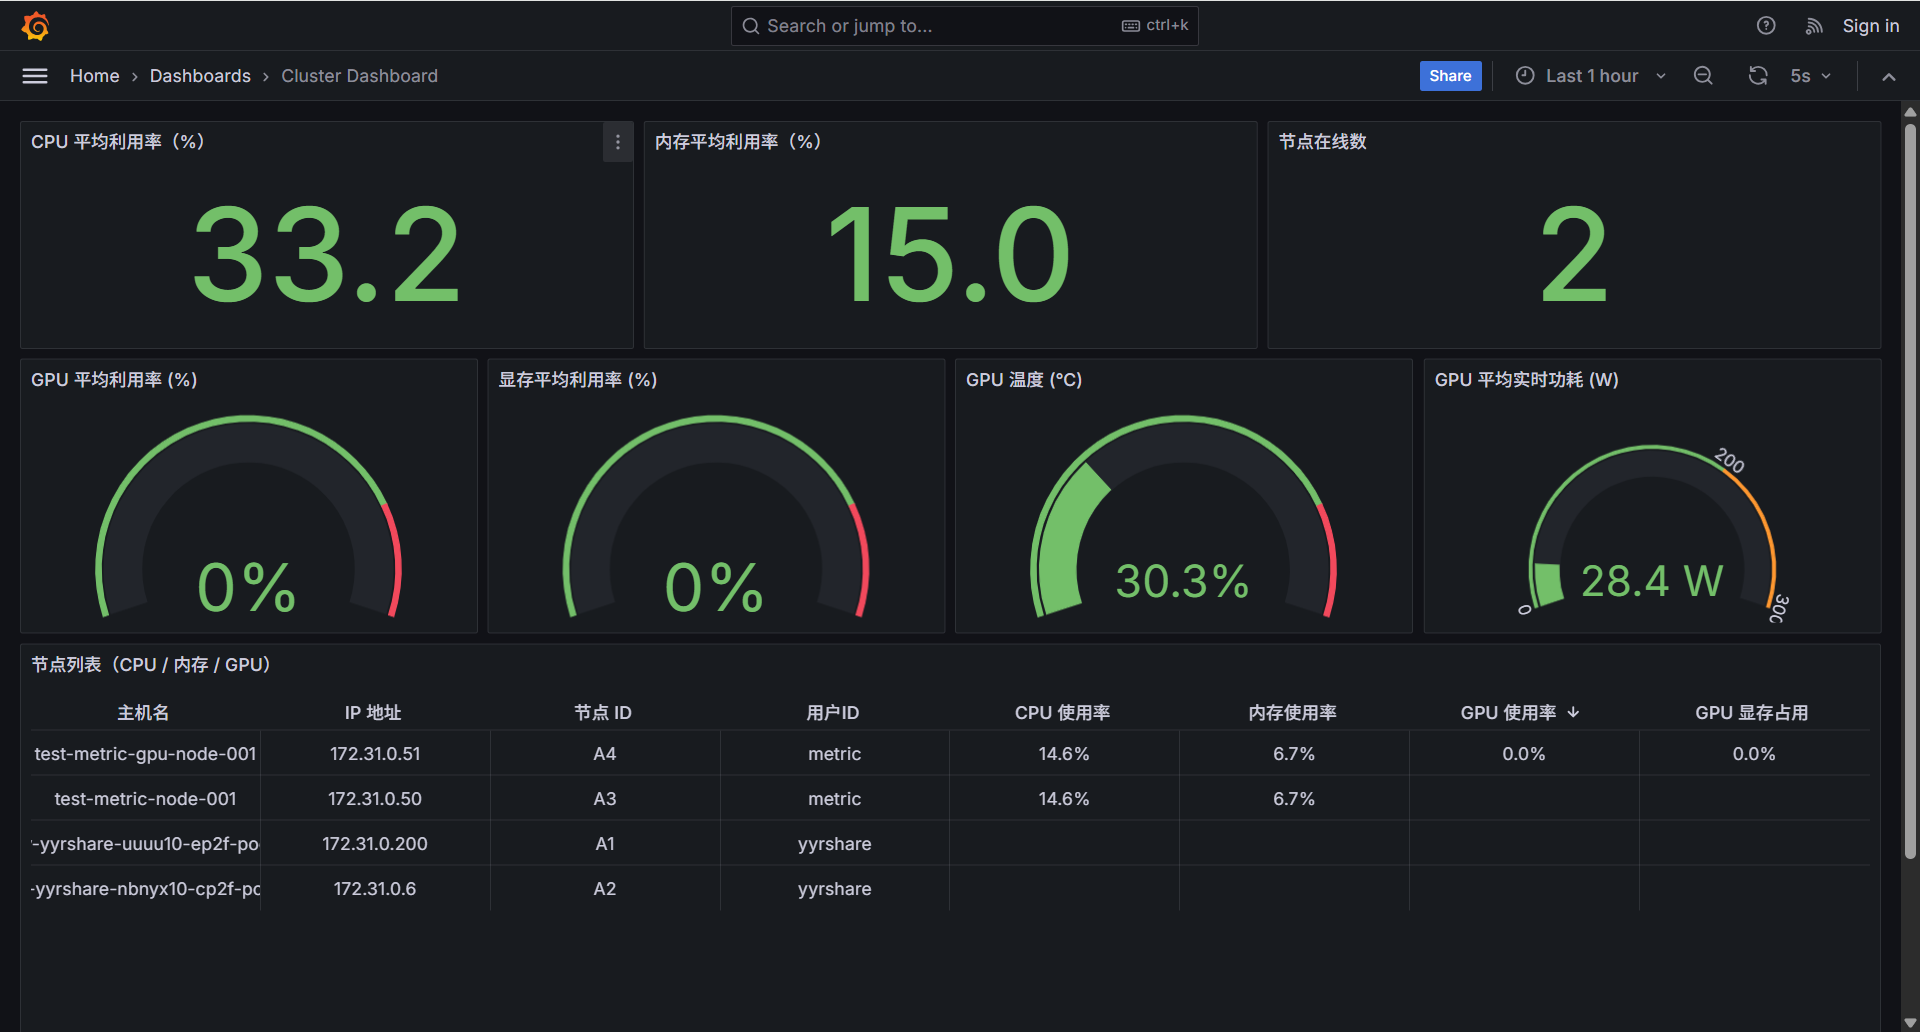 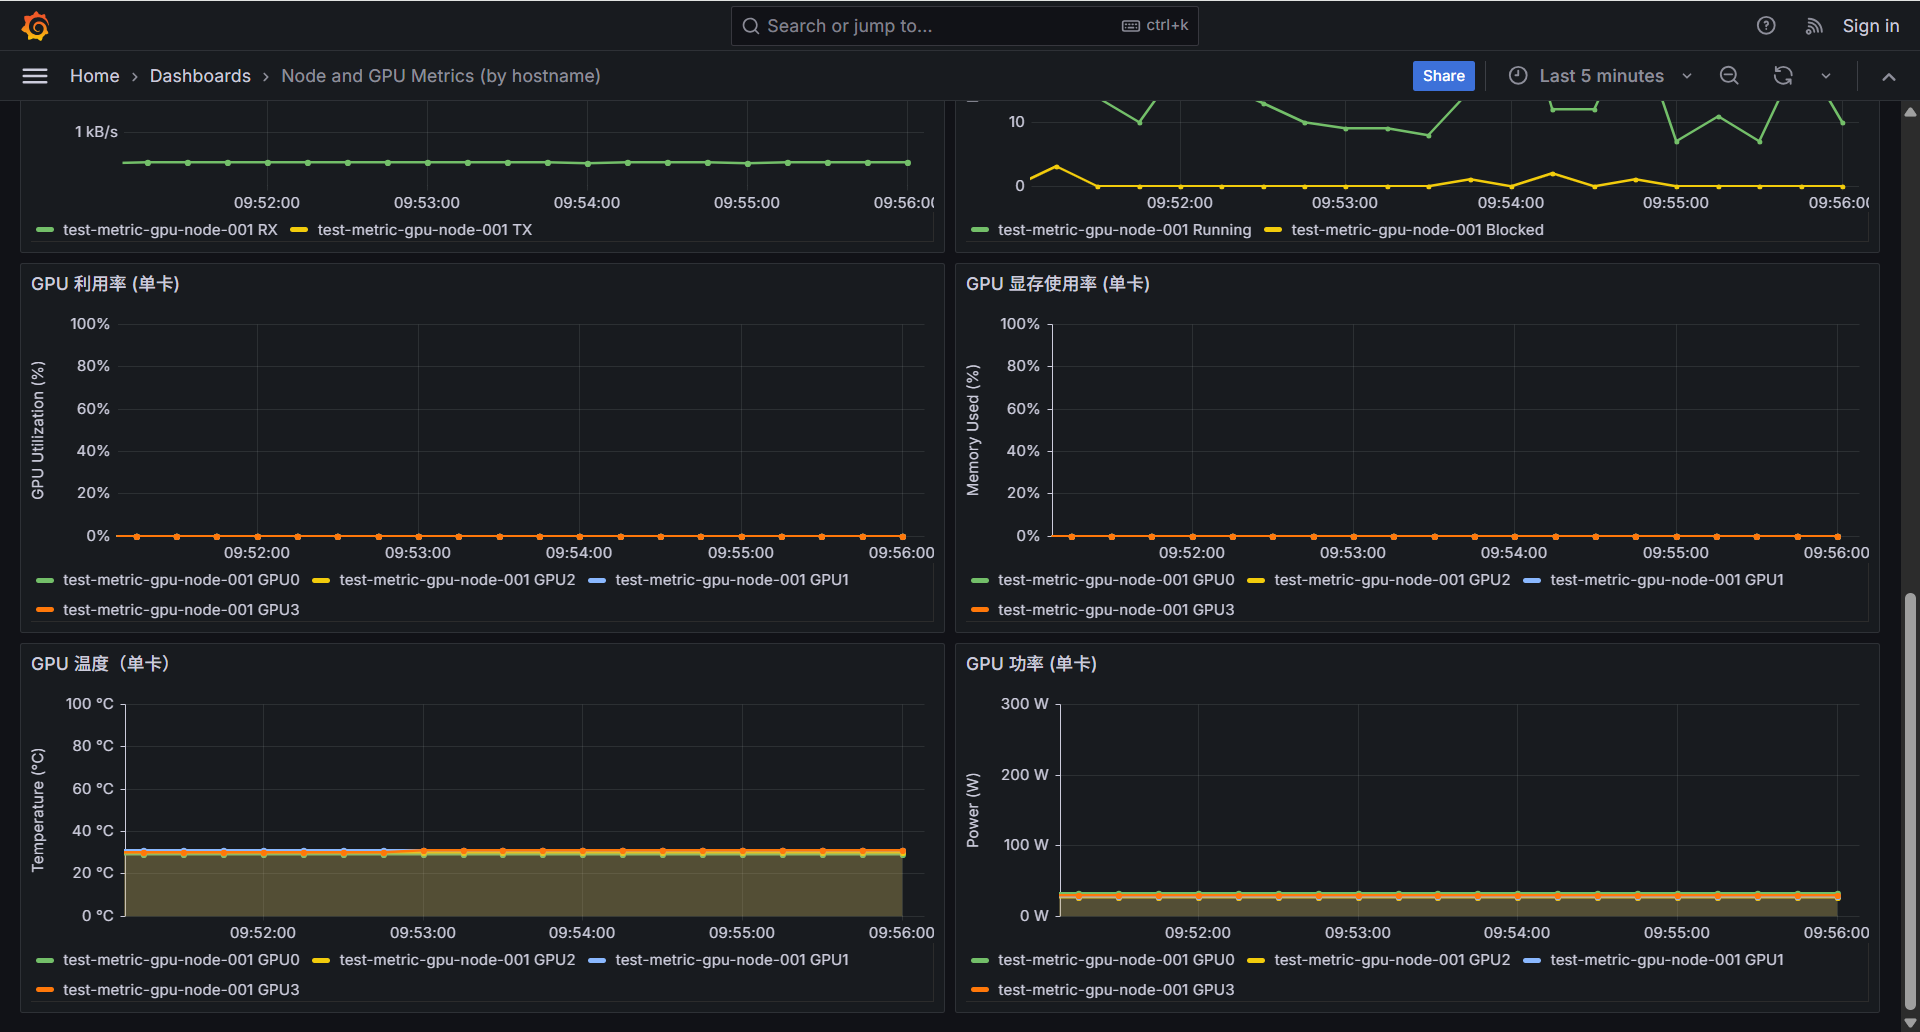 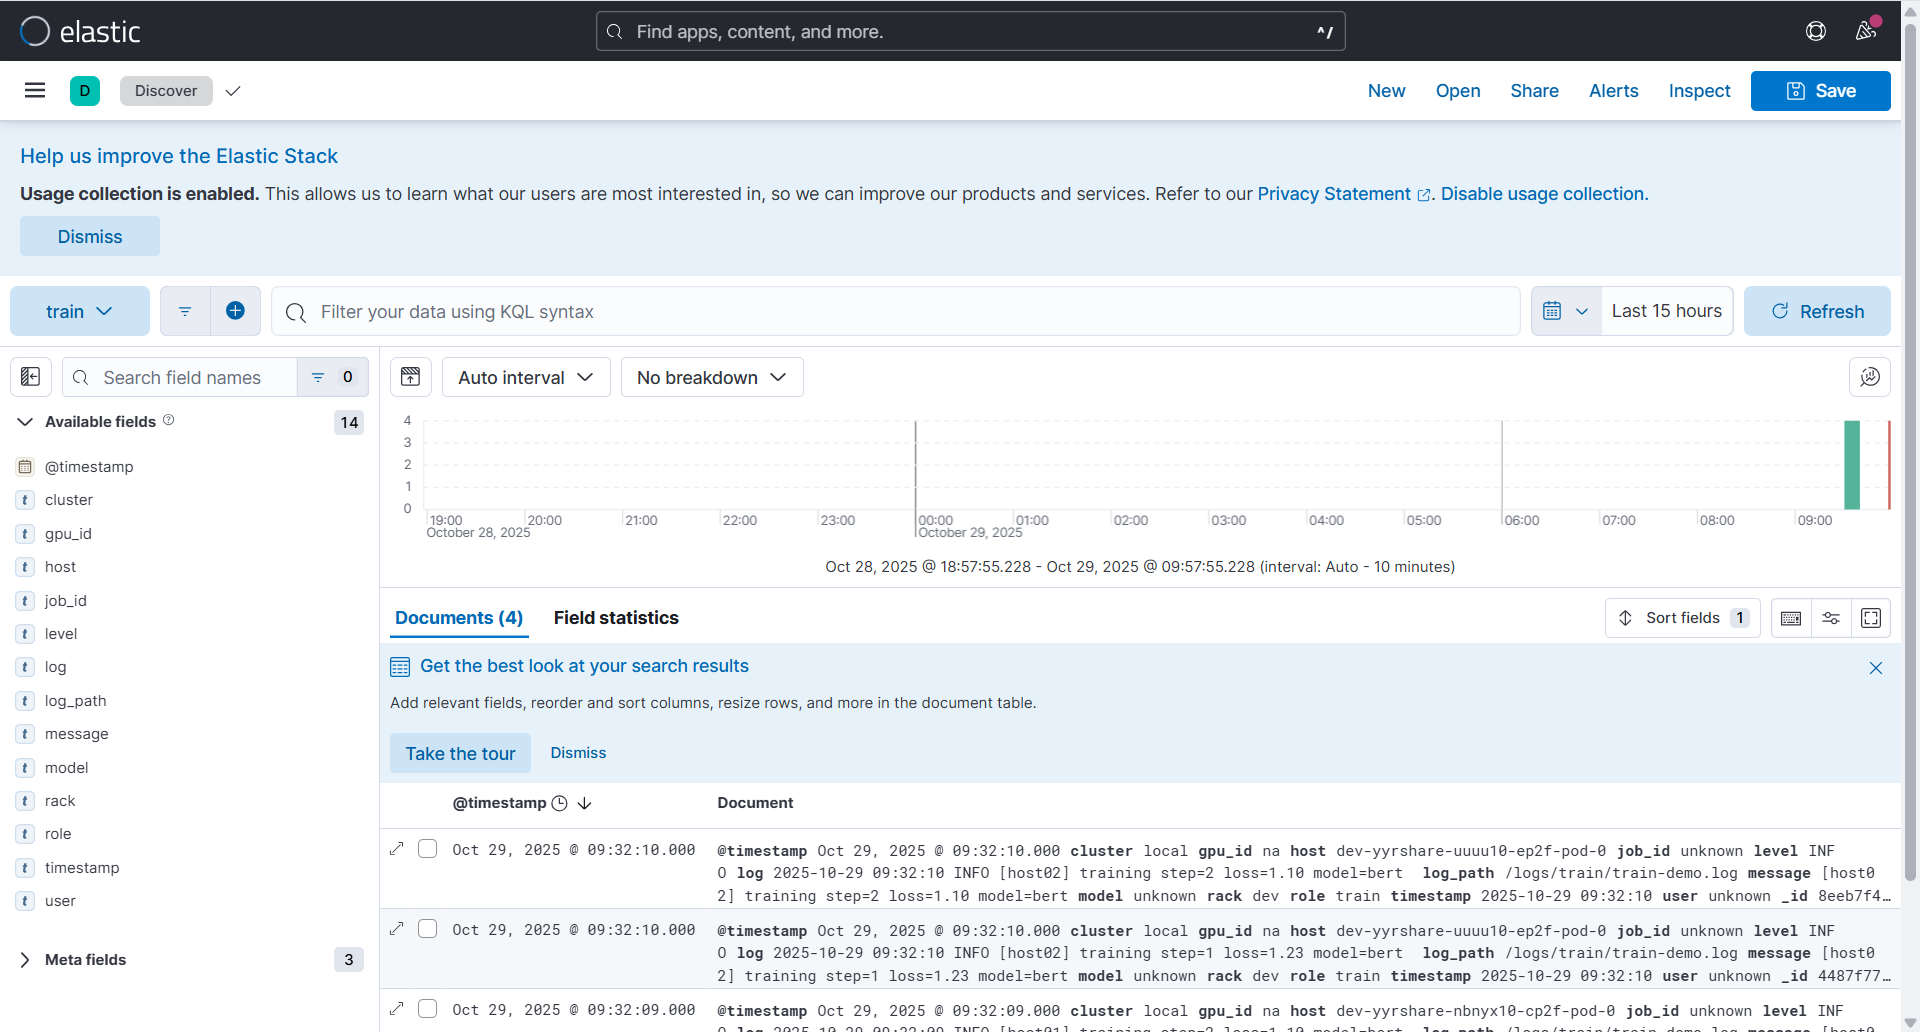 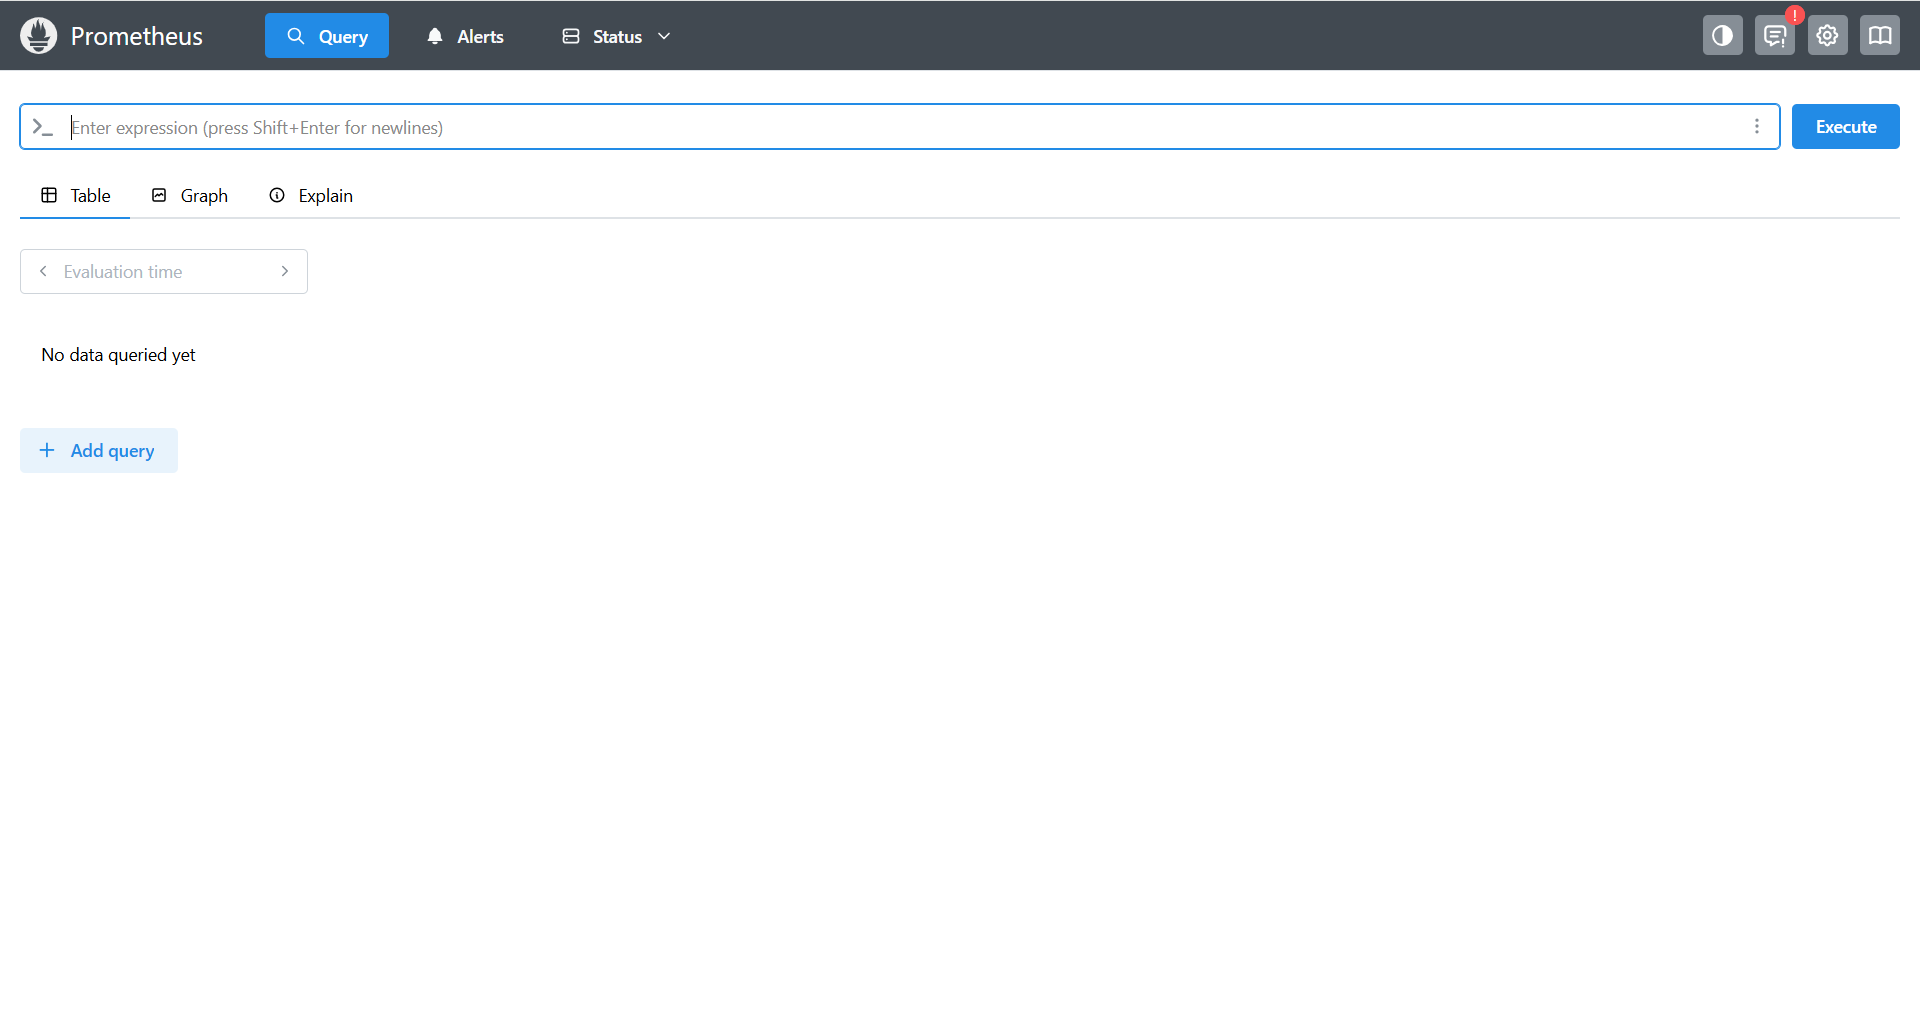  端到端测试通过: 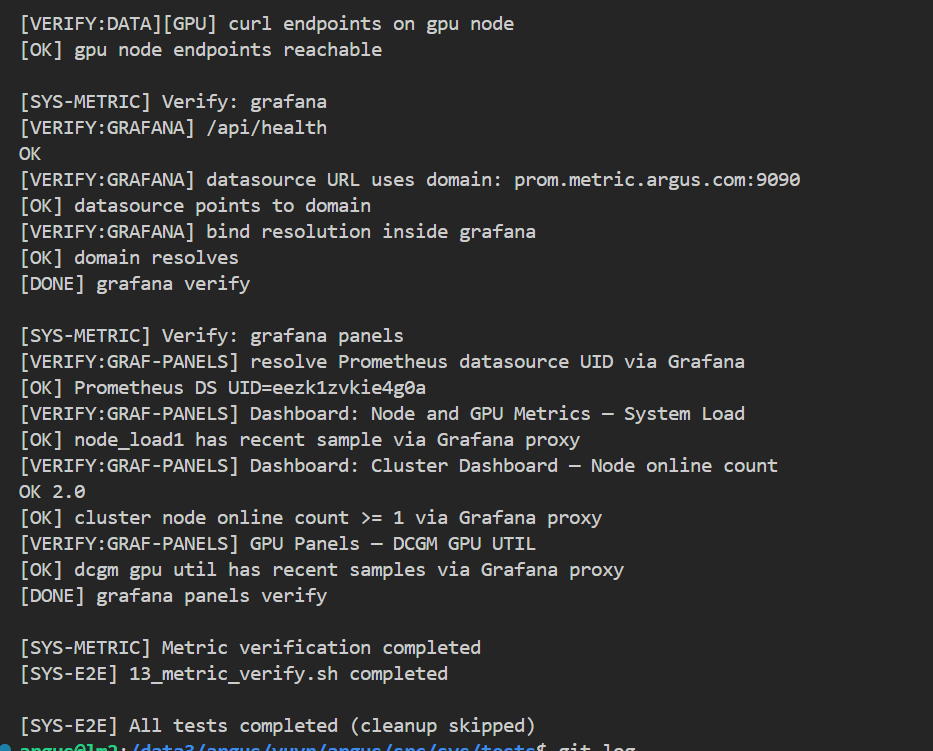 Co-authored-by: sundapeng.sdp <sundapeng@hashdata.cn> Reviewed-on: #35 Reviewed-by: xuxt <xuxt@zgclab.edu.cn> Reviewed-by: sundapeng <sundp@mail.zgclab.edu.cn> Reviewed-by: huhy <husteryezi@163.com>
111 lines
3.8 KiB
Docker
Executable File
111 lines
3.8 KiB
Docker
Executable File
FROM ubuntu/prometheus:3-24.04_stable
|
|
|
|
USER root
|
|
|
|
ARG USE_INTRANET=false
|
|
|
|
# 内网 apt 源配置
|
|
RUN if [ "$USE_INTRANET" = "true" ]; then \
|
|
echo "Configuring intranet apt sources..." && \
|
|
cp /etc/apt/sources.list /etc/apt/sources.list.bak && \
|
|
echo "deb [trusted=yes] http://10.68.64.1/ubuntu2204/ jammy main" > /etc/apt/sources.list && \
|
|
echo 'Acquire::https::Verify-Peer "false";' > /etc/apt/apt.conf.d/99disable-ssl-check && \
|
|
echo 'Acquire::https::Verify-Host "false";' >> /etc/apt/apt.conf.d/99disable-ssl-check; \
|
|
fi
|
|
|
|
# 验证源配置并安装常用工具
|
|
RUN echo "=== Current apt sources ===" && \
|
|
cat /etc/apt/sources.list && \
|
|
echo "=== Updating package list ===" && \
|
|
apt-get update && \
|
|
echo "=== Installing packages ===" && \
|
|
apt-get install -y --no-install-recommends \
|
|
supervisor \
|
|
net-tools \
|
|
inetutils-ping \
|
|
vim \
|
|
python3 \
|
|
python3-pip && \
|
|
apt-get clean && \
|
|
rm -rf /var/lib/apt/lists/* /tmp/* /var/tmp/*
|
|
|
|
# 如果是部署环境替换 apt 源
|
|
RUN if [ "$USE_INTRANET" = "true" ]; then \
|
|
echo "deb [trusted=yes] https://10.92.132.52/mirrors/ubuntu2204/ jammy main" > /etc/apt/sources.list; \
|
|
fi
|
|
|
|
# supervisor 日志目录
|
|
RUN mkdir -p /var/log/supervisor
|
|
|
|
# 设置 Prometheus 基础路径环境变量
|
|
ENV PROMETHEUS_BASE_PATH=/private/argus/metric/prometheus
|
|
|
|
# 设置用户和组ID环境变量
|
|
ARG ARGUS_BUILD_UID=2133
|
|
ARG ARGUS_BUILD_GID=2015
|
|
|
|
ENV ARGUS_BUILD_UID=${ARGUS_BUILD_UID} \
|
|
ARGUS_BUILD_GID=${ARGUS_BUILD_GID}
|
|
# 创建目录结构
|
|
RUN mkdir -p ${PROMETHEUS_BASE_PATH}/rules \
|
|
&& mkdir -p ${PROMETHEUS_BASE_PATH}/targets \
|
|
&& mkdir -p /private/argus/etc \
|
|
&& rm -rf /prometheus \
|
|
&& ln -s ${PROMETHEUS_BASE_PATH} /prometheus
|
|
|
|
# 修改 Prometheus 用户 UID/GID 并授权
|
|
RUN set -eux; \
|
|
existing_user=""; \
|
|
if getent passwd "${ARGUS_BUILD_UID}" >/dev/null 2>&1; then \
|
|
existing_user="$(getent passwd "${ARGUS_BUILD_UID}" | cut -d: -f1)"; \
|
|
fi; \
|
|
if [ -n "$existing_user" ] && [ "$existing_user" != "nobody" ]; then \
|
|
userdel -r "$existing_user" || true; \
|
|
fi; \
|
|
existing_group=""; \
|
|
if getent group "${ARGUS_BUILD_GID}" >/dev/null 2>&1; then \
|
|
existing_group="$(getent group "${ARGUS_BUILD_GID}" | cut -d: -f1)"; \
|
|
fi; \
|
|
if [ -n "$existing_group" ] && [ "$existing_group" != "nogroup" ]; then \
|
|
groupdel "$existing_group" || true; \
|
|
fi; \
|
|
usermod -u ${ARGUS_BUILD_UID} nobody; \
|
|
groupmod -g ${ARGUS_BUILD_GID} nogroup; \
|
|
chown -h nobody:nogroup /prometheus; \
|
|
chown -R nobody:nogroup ${PROMETHEUS_BASE_PATH}; \
|
|
chown -R nobody:nogroup /etc/prometheus
|
|
|
|
# supervisor 配置
|
|
COPY supervisord.conf /etc/supervisor/conf.d/supervisord.conf
|
|
|
|
# 启动脚本
|
|
COPY start-prometheus-supervised.sh /usr/local/bin/start-prometheus-supervised.sh
|
|
RUN chmod +x /usr/local/bin/start-prometheus-supervised.sh && \
|
|
chown nobody:nogroup /usr/local/bin/start-prometheus-supervised.sh
|
|
|
|
# targets 更新脚本
|
|
COPY start-targets-updater.sh /usr/local/bin/start-targets-updater.sh
|
|
RUN chmod +x /usr/local/bin/start-targets-updater.sh && \
|
|
chown nobody:nogroup /usr/local/bin/start-targets-updater.sh
|
|
|
|
# targets 更新 Python 脚本
|
|
COPY update_targets.py /usr/local/bin/update_targets.py
|
|
RUN chmod +x /usr/local/bin/update_targets.py && \
|
|
chown nobody:nogroup /usr/local/bin/update_targets.py
|
|
|
|
# exporter 配置文件 - 复制到内部目录
|
|
COPY exporter_config.json /usr/local/bin/exporter_config.json
|
|
|
|
COPY prometheus.yml /etc/prometheus/prometheus.yml
|
|
|
|
RUN chown nobody:nogroup /usr/local/bin/exporter_config.json /etc/prometheus/prometheus.yml
|
|
|
|
COPY dns-monitor.sh /usr/local/bin/dns-monitor.sh
|
|
RUN chmod +x /usr/local/bin/dns-monitor.sh
|
|
|
|
USER root
|
|
|
|
EXPOSE 9090
|
|
|
|
ENTRYPOINT ["/usr/bin/supervisord", "-c", "/etc/supervisor/conf.d/supervisord.conf", "-n"]
|