完成a6000测试系统构建、部署、测试整合 (#35)
测试方案: - lm2机器端口映射到本机:18080, 18081, 8082-8085 - 访问URL: http://localhost:18080/dashboard 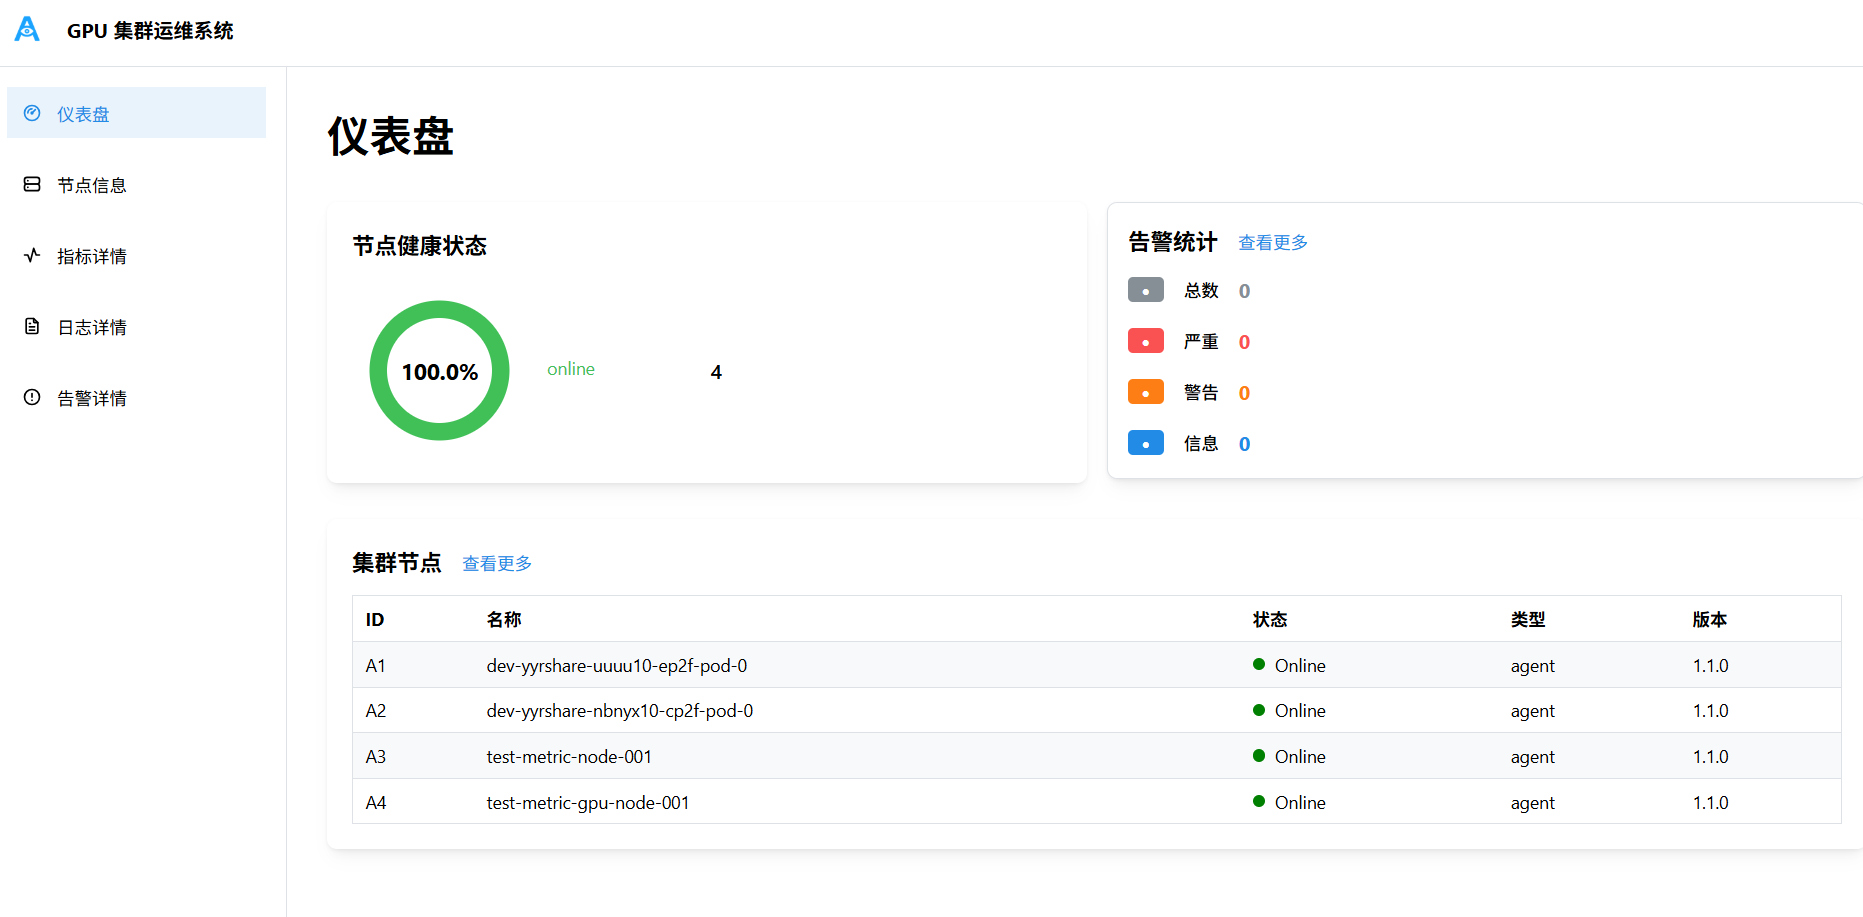 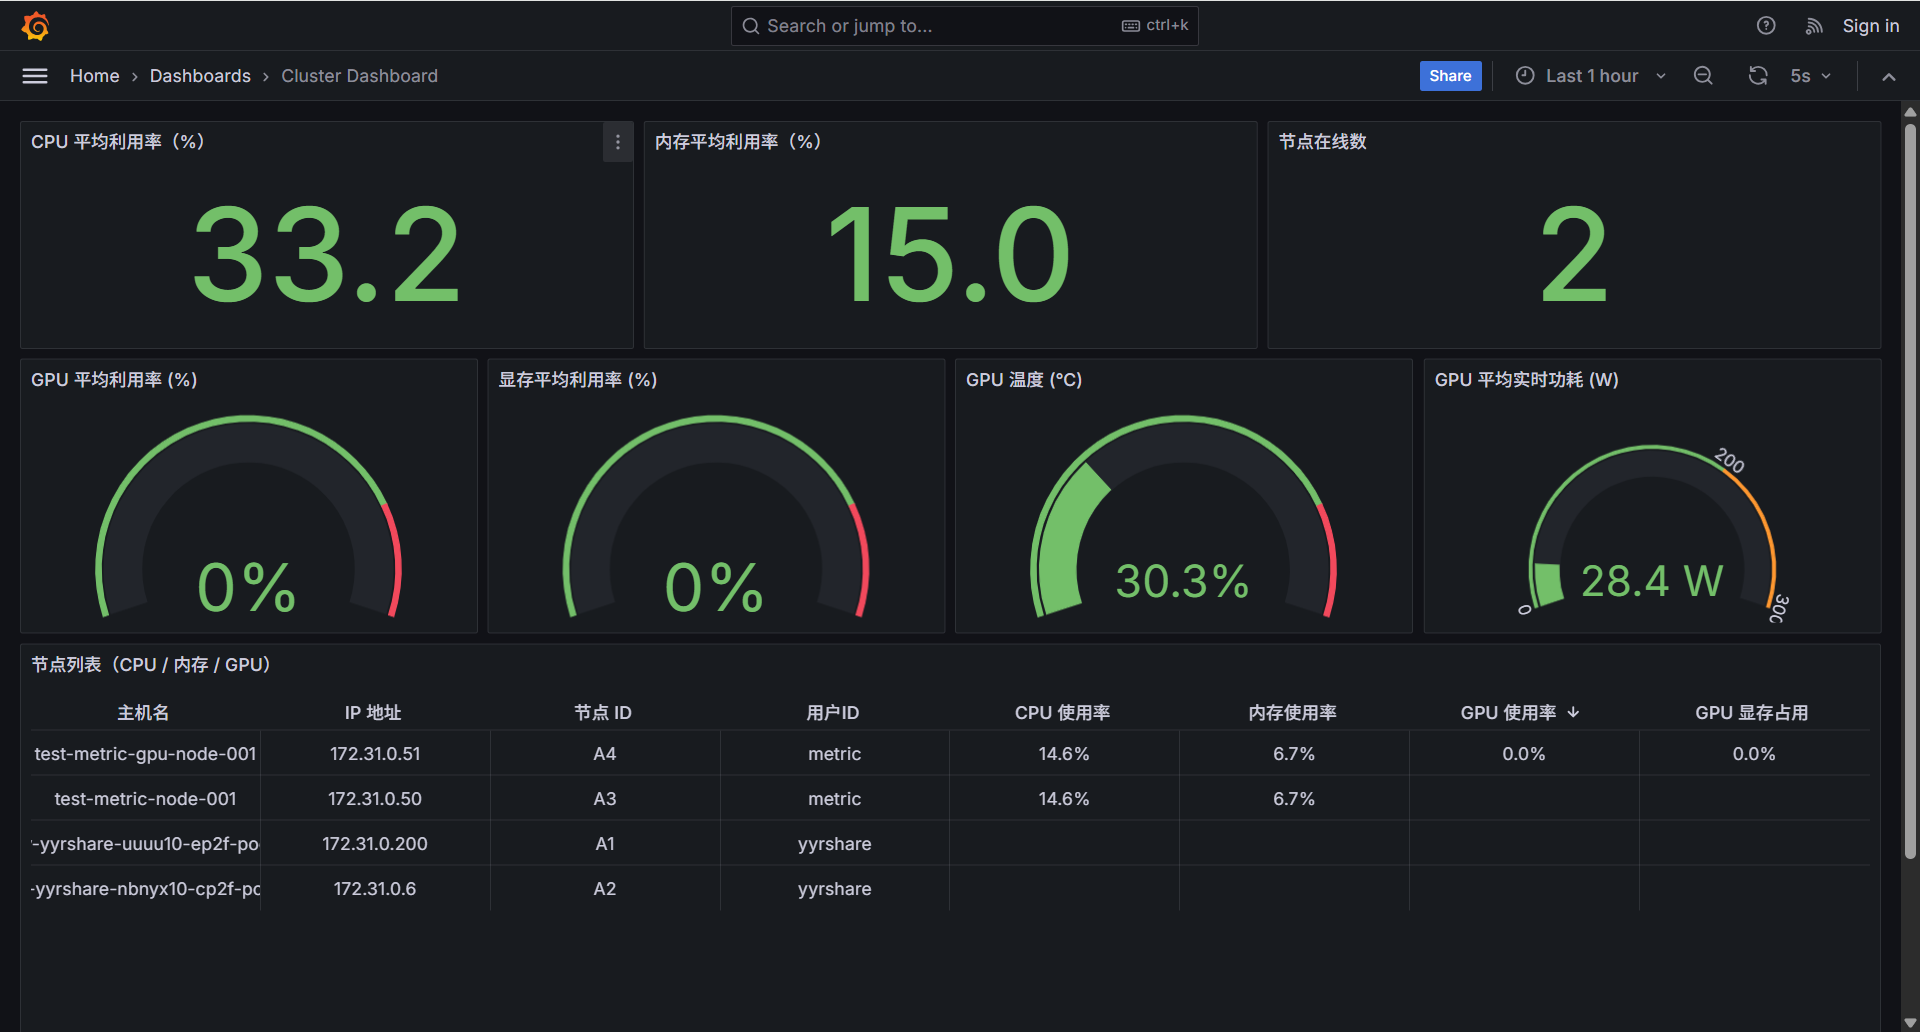 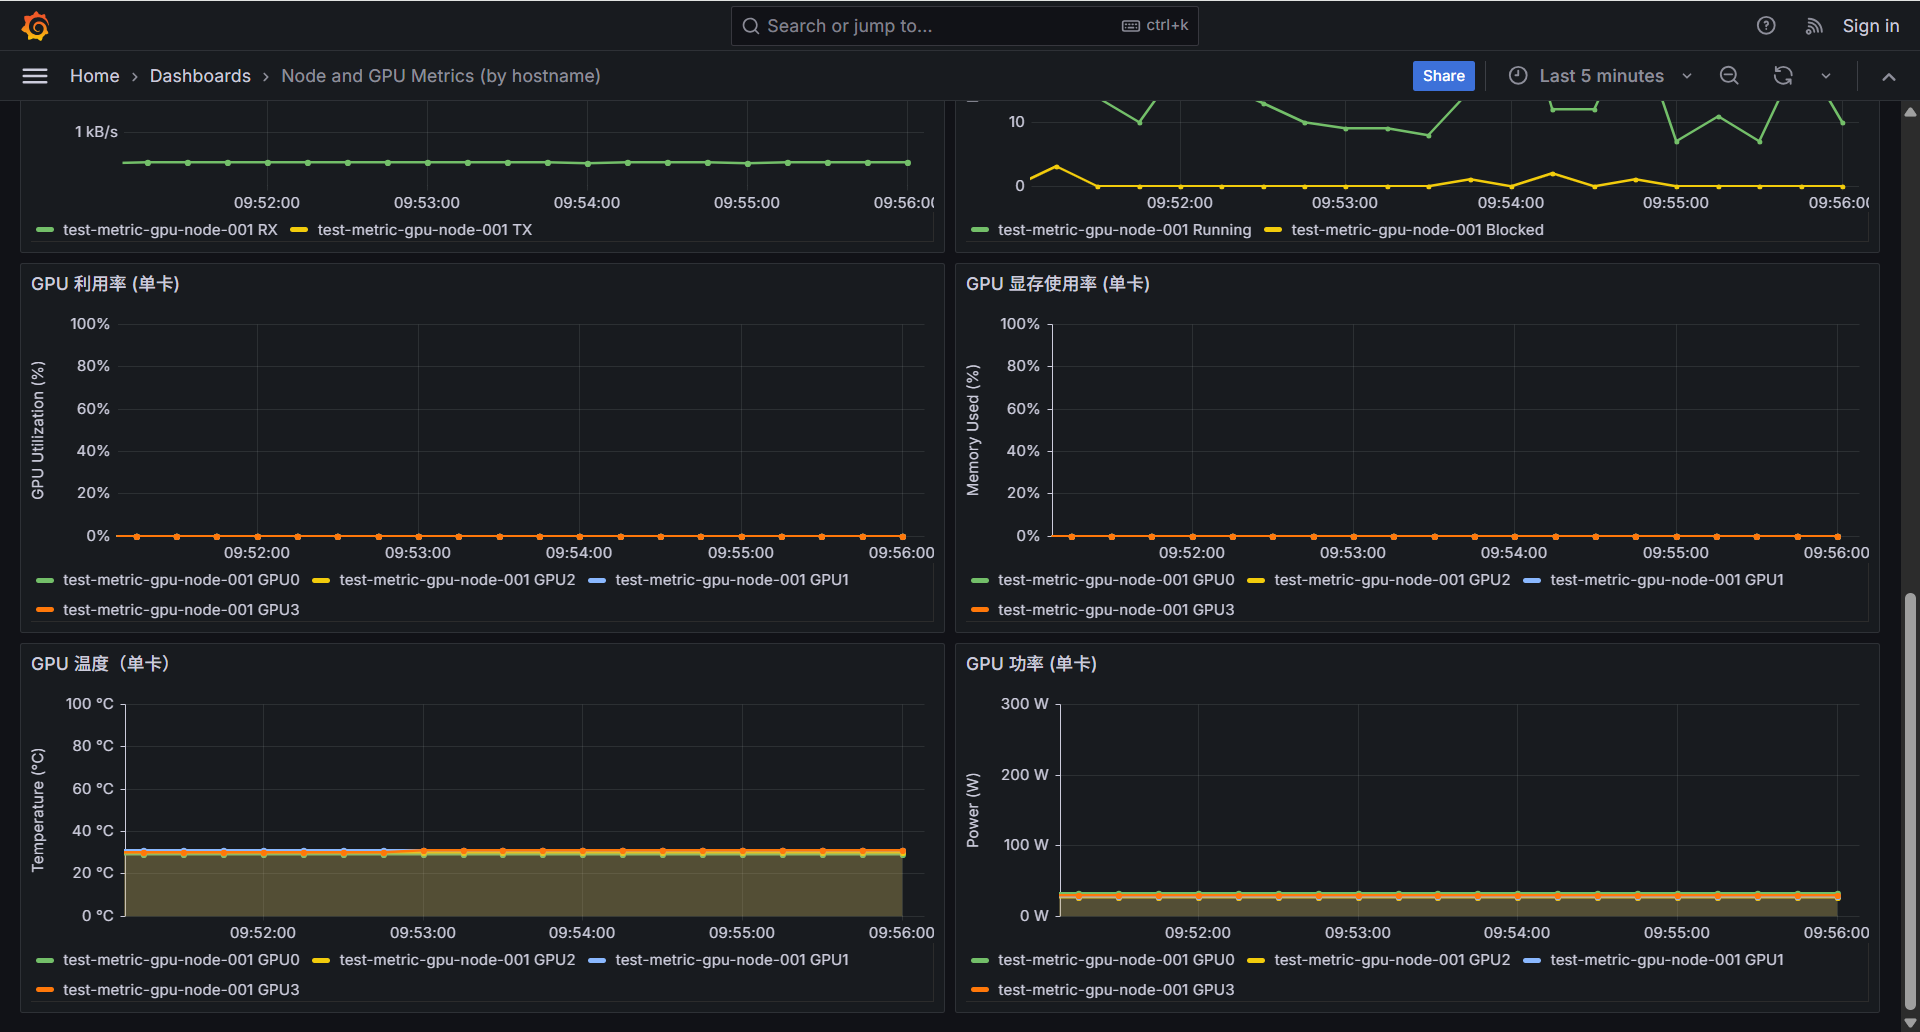 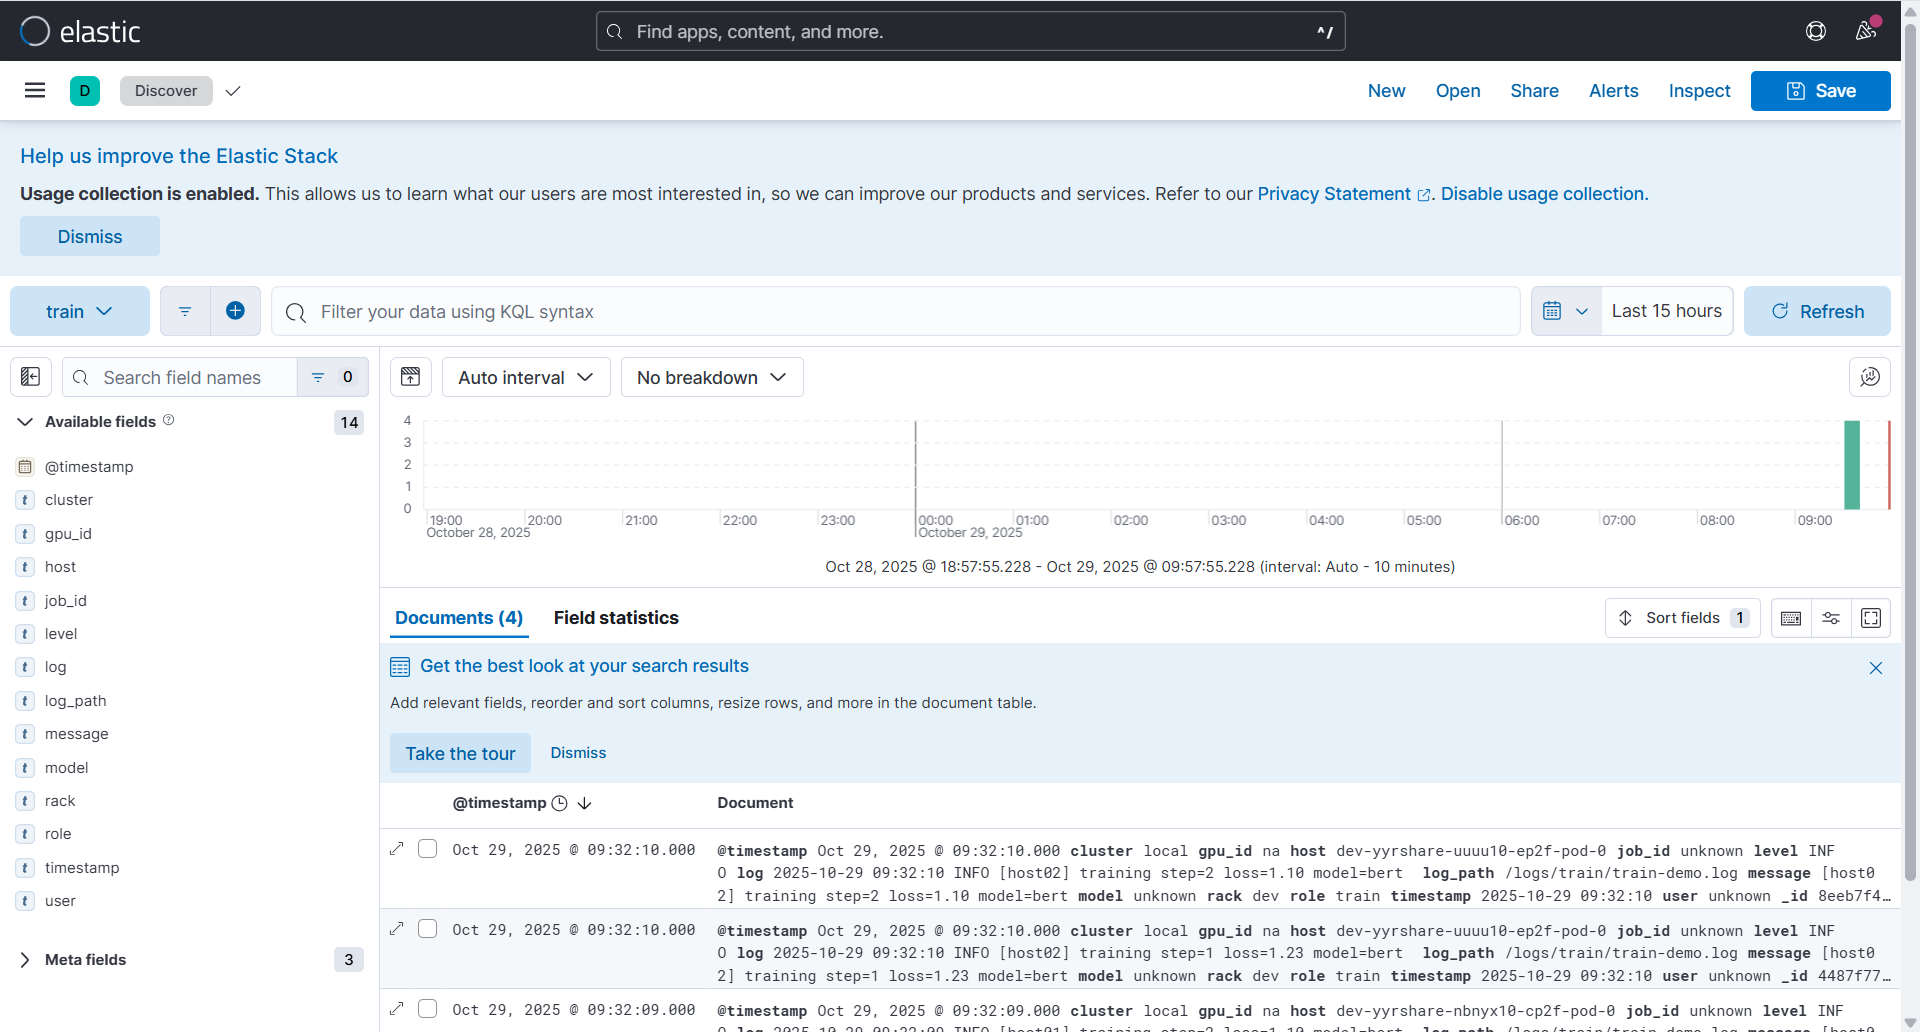 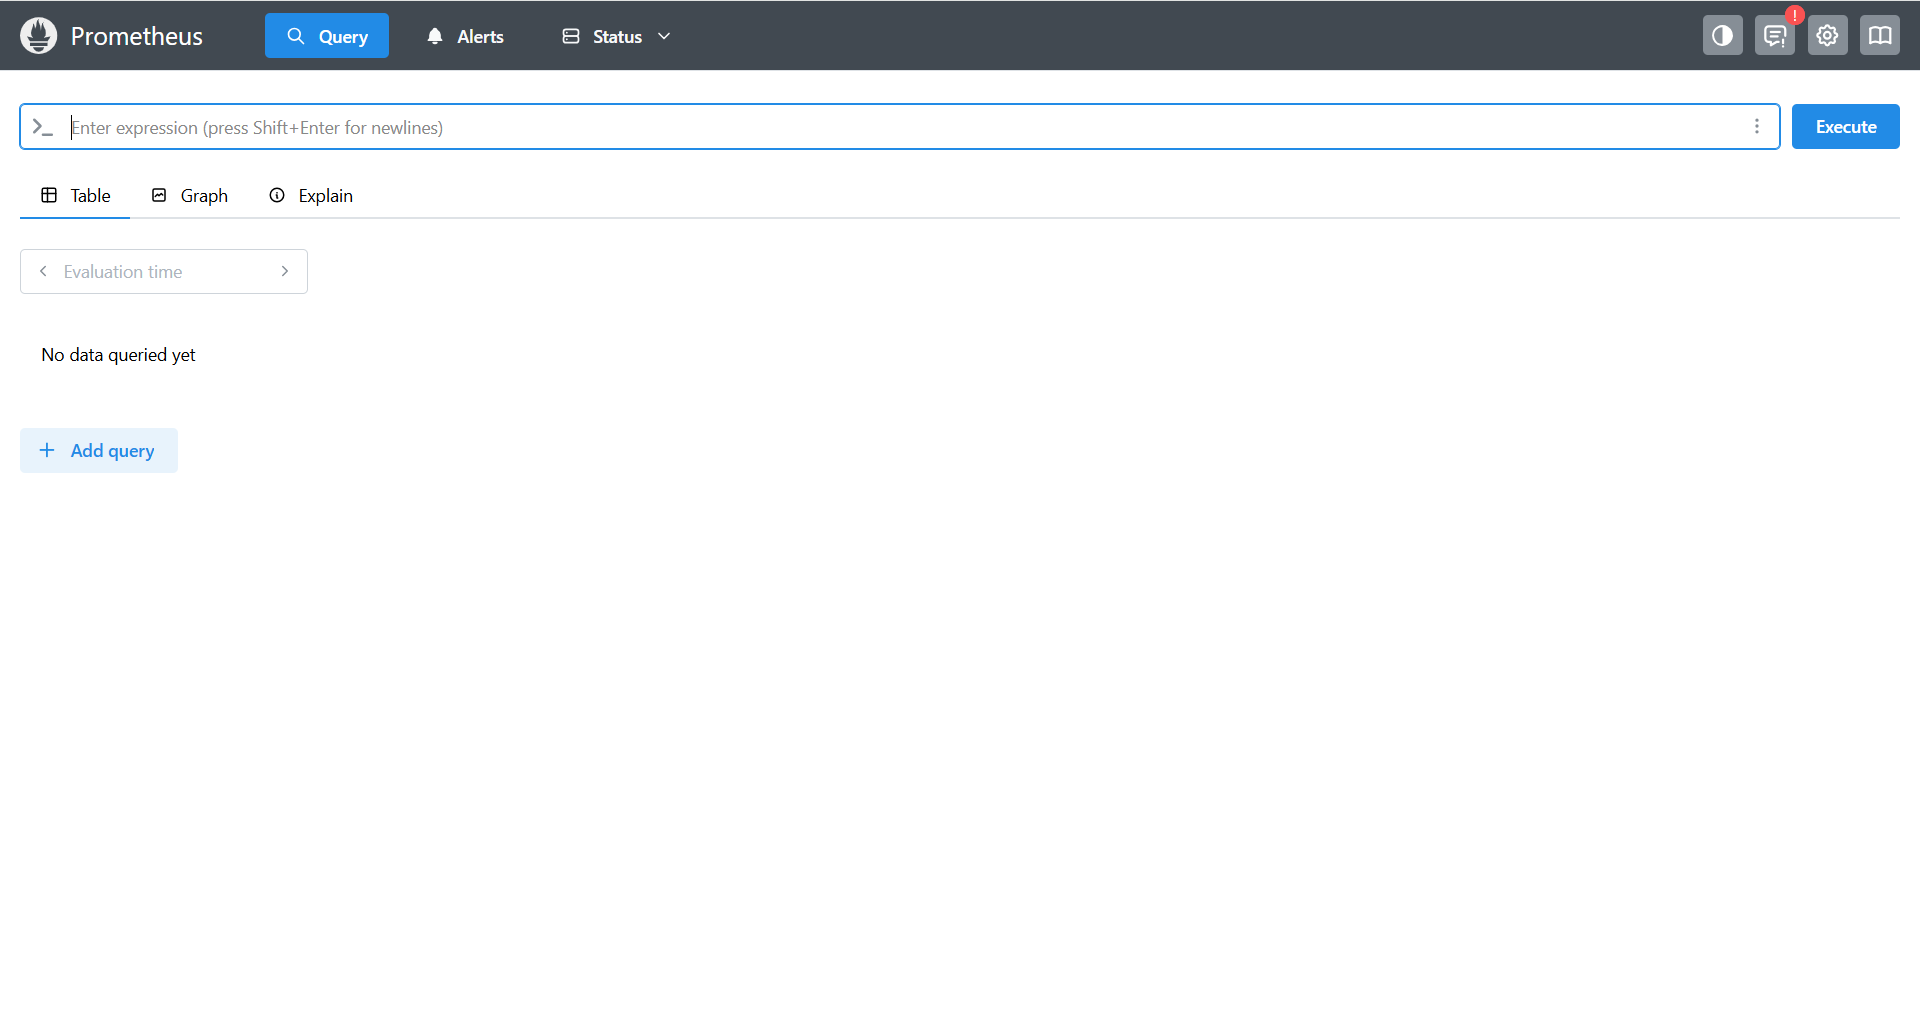 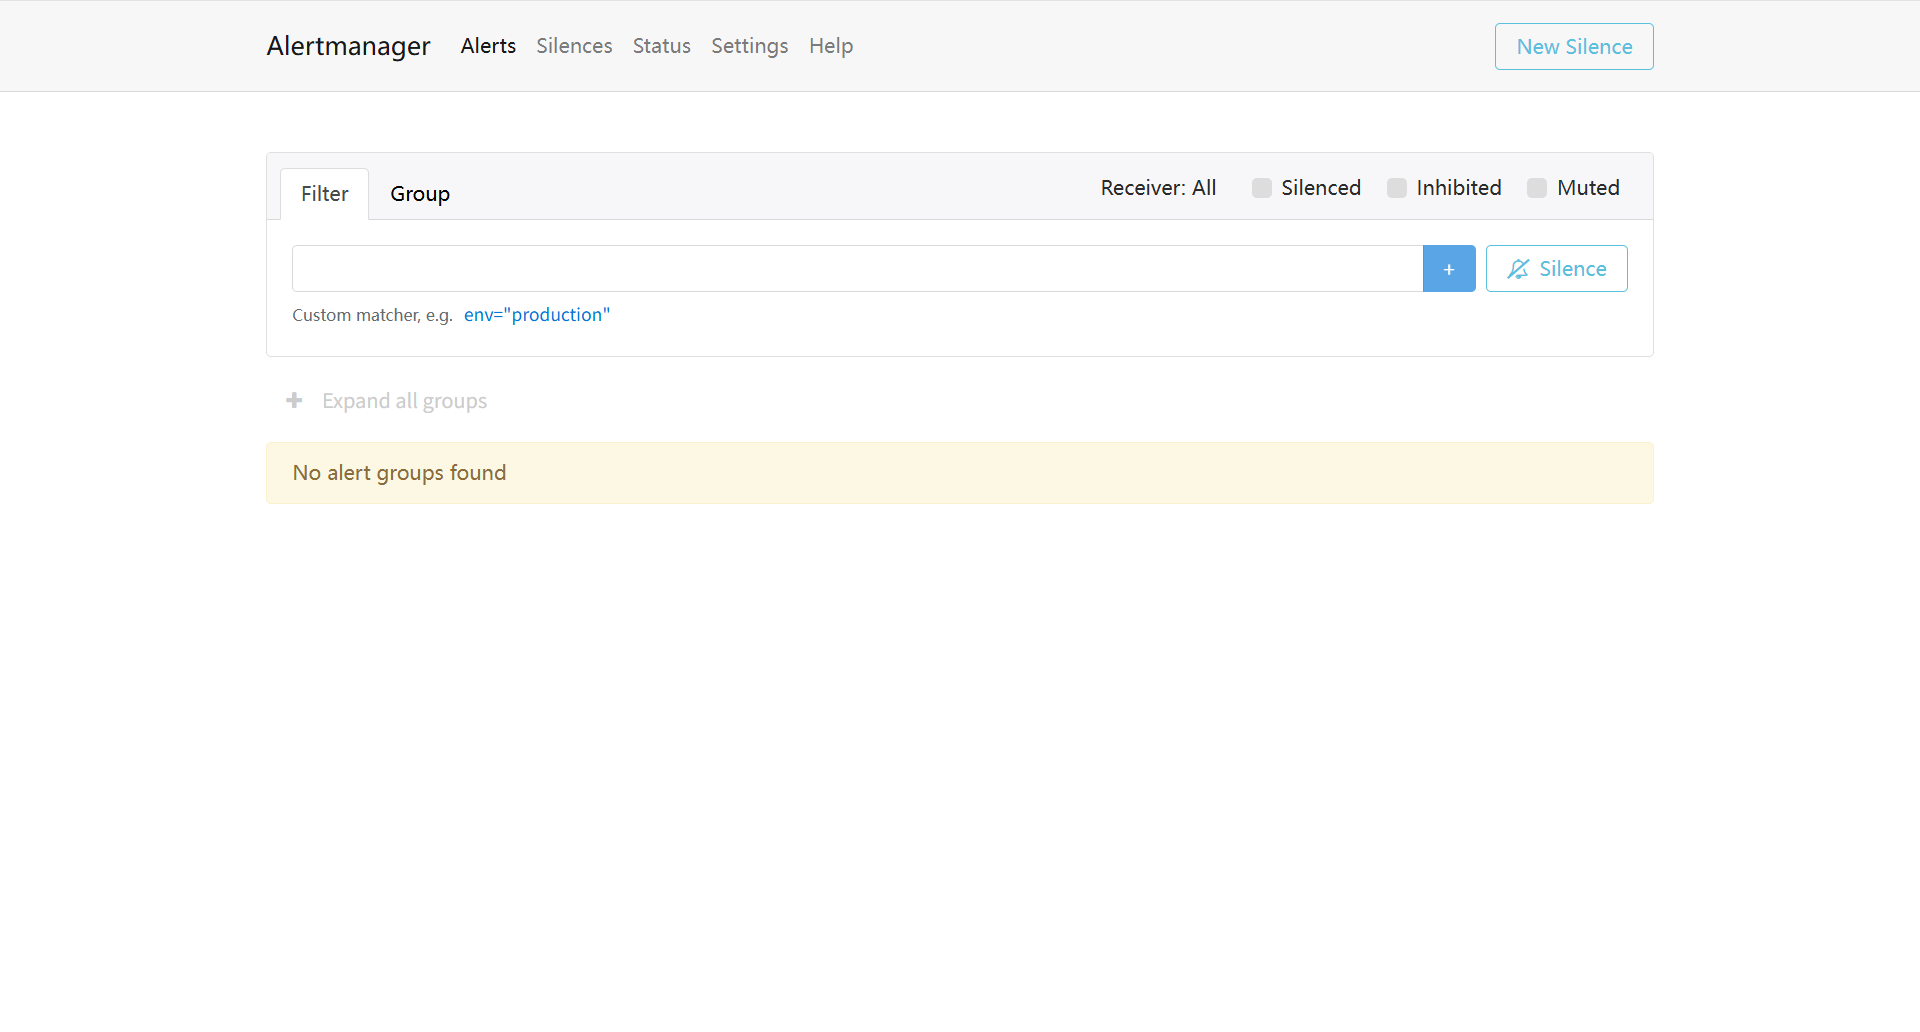 端到端测试通过: 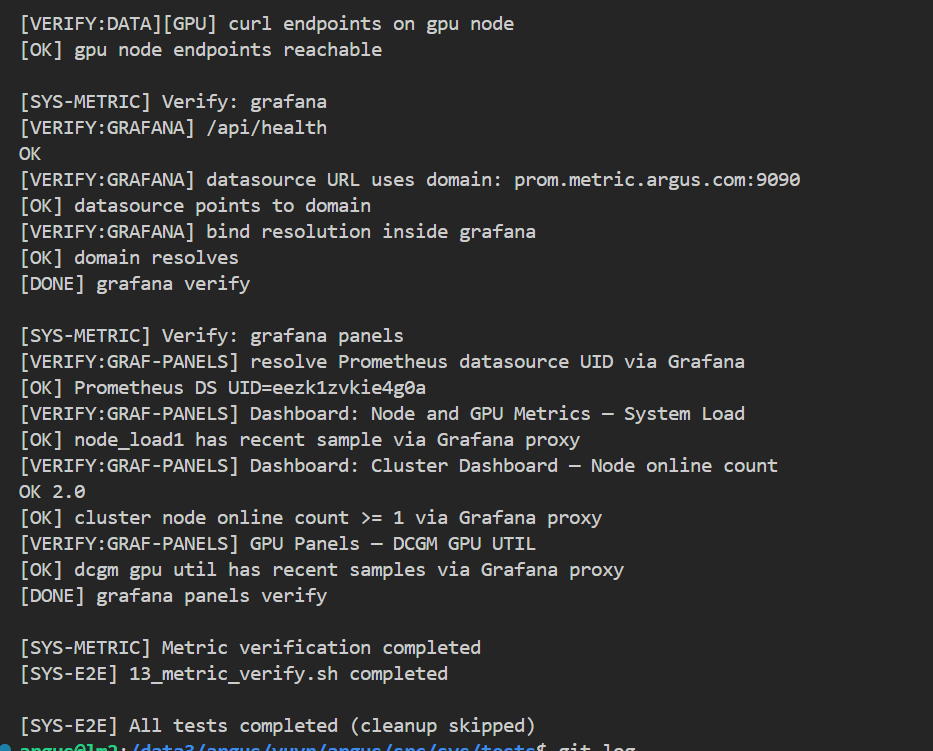 Co-authored-by: sundapeng.sdp <sundapeng@hashdata.cn> Reviewed-on: #35 Reviewed-by: xuxt <xuxt@zgclab.edu.cn> Reviewed-by: sundapeng <sundp@mail.zgclab.edu.cn> Reviewed-by: huhy <husteryezi@163.com>
This commit was merged in pull request #35.
This commit is contained in:

@@ -24,24 +24,37 @@ RUN apt-get update && \
|
||||
apt-get clean && rm -rf /var/lib/apt/lists/*
|
||||
|
||||
ENV FRONTEND_BASE_PATH=/private/argus/web/frontend
|
||||
ARG ARGUS_UID=2133
|
||||
ARG ARGUS_GID=2015
|
||||
ENV ARGUS_UID=${ARGUS_UID}
|
||||
ENV ARGUS_GID=${ARGUS_GID}
|
||||
ARG ARGUS_BUILD_UID=2133
|
||||
ARG ARGUS_BUILD_GID=2015
|
||||
ENV ARGUS_BUILD_UID=${ARGUS_BUILD_UID}
|
||||
ENV ARGUS_BUILD_GID=${ARGUS_BUILD_GID}
|
||||
|
||||
RUN mkdir -p ${FRONTEND_BASE_PATH} && \
|
||||
mkdir -p /private/argus/etc
|
||||
|
||||
# 创建 web 用户(可自定义 UID/GID)
|
||||
# 创建 web 用户组
|
||||
RUN groupadd -g ${ARGUS_GID} web
|
||||
|
||||
# 创建 web 用户并指定组
|
||||
RUN useradd -M -s /usr/sbin/nologin -u ${ARGUS_UID} -g ${ARGUS_GID} web
|
||||
|
||||
RUN chown -R web:web ${FRONTEND_BASE_PATH} && \
|
||||
chown -R web:web /private/argus/etc && \
|
||||
chown -R web:web /usr/local/bin
|
||||
RUN set -eux; \
|
||||
# 确保目标 GID 存在(组名可不固定)\
|
||||
if ! getent group "${ARGUS_BUILD_GID}" >/dev/null; then \
|
||||
groupadd -g "${ARGUS_BUILD_GID}" web || true; \
|
||||
fi; \
|
||||
# 若存在 web 用户则尽量对齐 UID/GID;否则仅在 UID 未被占用时创建
|
||||
if id web >/dev/null 2>&1; then \
|
||||
current_uid="$(id -u web)"; \
|
||||
if [ "$current_uid" != "${ARGUS_BUILD_UID}" ] && ! getent passwd "${ARGUS_BUILD_UID}" >/dev/null; then \
|
||||
usermod -u "${ARGUS_BUILD_UID}" web; \
|
||||
fi; \
|
||||
usermod -g "${ARGUS_BUILD_GID}" web || true; \
|
||||
else \
|
||||
if ! getent passwd "${ARGUS_BUILD_UID}" >/dev/null; then \
|
||||
useradd -M -s /usr/sbin/nologin -u "${ARGUS_BUILD_UID}" -g "${ARGUS_BUILD_GID}" web; \
|
||||
else \
|
||||
echo "UID ${ARGUS_BUILD_UID} already exists; skip creating user 'web'"; \
|
||||
fi; \
|
||||
fi; \
|
||||
# 用数值 UID:GID 赋权,避免依赖用户名/组名
|
||||
chown -R "${ARGUS_BUILD_UID}:${ARGUS_BUILD_GID}" ${FRONTEND_BASE_PATH} /private/argus/etc /usr/local/bin || true
|
||||
|
||||
# 配置内网 apt 源 (如果指定了内网选项)
|
||||
RUN if [ "$USE_INTRANET" = "true" ]; then \
|
||||
|
||||
@@ -4,7 +4,7 @@ docker pull ubuntu:24.04
|
||||
source src/web/tests/.env
|
||||
|
||||
docker build \
|
||||
--build-arg ARGUS_UID=${ARGUS_UID} \
|
||||
--build-arg ARGUS_GID=${ARGUS_GID} \
|
||||
--build-arg ARGUS_BUILD_UID=${ARGUS_BUILD_UID} \
|
||||
--build-arg ARGUS_BUILD_GID=${ARGUS_BUILD_GID} \
|
||||
-f src/web/build_tools/frontend/Dockerfile -t argus-web-frontend:latest .
|
||||
docker save -o argus-web-frontend-latest.tar argus-web-frontend:latest
|
||||
|
||||
@@ -1,4 +1,4 @@
|
||||
user web;
|
||||
user root;
|
||||
worker_processes auto;
|
||||
|
||||
events {
|
||||
|
||||
@@ -8,8 +8,8 @@ DNS_SCRIPT="${DNS_DIR}/update-dns.sh"
|
||||
DOMAIN=web.argus.com
|
||||
WEB_DOMAIN_FILE="${DNS_DIR}/${DOMAIN}"
|
||||
RUNTIME_USER="${ARGUS_RUNTIME_USER:-argus}"
|
||||
RUNTIME_UID="${ARGUS_UID:-2133}"
|
||||
RUNTIME_GID="${ARGUS_GID:-2015}"
|
||||
RUNTIME_UID="${ARGUS_BUILD_UID:-2133}"
|
||||
RUNTIME_GID="${ARGUS_BUILD_GID:-2015}"
|
||||
|
||||
mkdir -p "$DNS_DIR"
|
||||
chown -R "$RUNTIME_UID:$RUNTIME_GID" "$DNS_DIR" 2>/dev/null || true
|
||||
@@ -28,5 +28,26 @@ chmod 755 "$WEB_DOMAIN_FILE"
|
||||
|
||||
echo "[INFO] Launching nginx..."
|
||||
|
||||
# ========== 生成运行期前端配置 (/usr/share/nginx/html/argus-config.js) ==========
|
||||
CFG_JS="/usr/share/nginx/html/argus-config.js"
|
||||
MASTER_PORT="${EXTERNAL_MASTER_PORT:-8085}"
|
||||
ALERT_PORT="${EXTERNAL_ALERTMANAGER_PORT:-8084}"
|
||||
GRAFANA_PORT="${EXTERNAL_GRAFANA_PORT:-8081}"
|
||||
PROM_PORT="${EXTERNAL_PROMETHEUS_PORT:-8082}"
|
||||
KIBANA_PORT="${EXTERNAL_KIBANA_PORT:-8083}"
|
||||
{
|
||||
echo "// generated at runtime by start-web-supervised.sh"
|
||||
echo "window.__ARGUS_PORTS__ = {"
|
||||
echo " MASTER: ${MASTER_PORT},"
|
||||
echo " ALERTMANAGER: ${ALERT_PORT},"
|
||||
echo " GRAFANA: ${GRAFANA_PORT},"
|
||||
echo " PROMETHEUS: ${PROM_PORT},"
|
||||
echo " KIBANA: ${KIBANA_PORT},"
|
||||
echo "};"
|
||||
if [[ -n "${ARGUS_PUBLIC_HOST:-}" ]]; then
|
||||
printf "window.__ARGUS_PUBLIC_HOST__ = '%s';\n" "$ARGUS_PUBLIC_HOST"
|
||||
fi
|
||||
} > "$CFG_JS"
|
||||
|
||||
# 启动 nginx 前台模式
|
||||
exec /usr/sbin/nginx -g "daemon off;"
|
||||
|
||||
@@ -18,7 +18,7 @@ stopasgroup=true
|
||||
|
||||
[program:web-health]
|
||||
command=/usr/local/bin/health-check.sh
|
||||
user=web
|
||||
user=root
|
||||
stdout_logfile=/var/log/supervisor/web-health.log
|
||||
stderr_logfile=/var/log/supervisor/web-health_error.log
|
||||
autorestart=true
|
||||
|
||||
@@ -8,24 +8,34 @@ RUN apt-get update && \
|
||||
apt-get clean && rm -rf /var/lib/apt/lists/*
|
||||
|
||||
ENV FRONTEND_BASE_PATH=/private/argus/web/proxy
|
||||
ARG ARGUS_UID=2133
|
||||
ARG ARGUS_GID=2015
|
||||
ENV ARGUS_UID=${ARGUS_UID}
|
||||
ENV ARGUS_GID=${ARGUS_GID}
|
||||
ARG ARGUS_BUILD_UID=2133
|
||||
ARG ARGUS_BUILD_GID=2015
|
||||
ENV ARGUS_BUILD_UID=${ARGUS_BUILD_UID}
|
||||
ENV ARGUS_BUILD_GID=${ARGUS_BUILD_GID}
|
||||
|
||||
RUN mkdir -p ${FRONTEND_BASE_PATH} && \
|
||||
mkdir -p /private/argus/etc
|
||||
|
||||
# 创建 proxy 用户(可自定义 UID/GID)
|
||||
# 创建 proxy 用户组
|
||||
RUN groupadd -g ${ARGUS_GID} web_proxy
|
||||
|
||||
# 创建 proxy 用户并指定组
|
||||
RUN useradd -M -s /usr/sbin/nologin -u ${ARGUS_UID} -g ${ARGUS_GID} web_proxy
|
||||
|
||||
RUN chown -R web_proxy:web_proxy ${FRONTEND_BASE_PATH} && \
|
||||
chown -R web_proxy:web_proxy /private/argus/etc && \
|
||||
chown -R web_proxy:web_proxy /usr/local/bin
|
||||
RUN set -eux; \
|
||||
if ! getent group "${ARGUS_BUILD_GID}" >/dev/null; then \
|
||||
groupadd -g "${ARGUS_BUILD_GID}" web_proxy || true; \
|
||||
fi; \
|
||||
if id web_proxy >/dev/null 2>&1; then \
|
||||
current_uid="$(id -u web_proxy)"; \
|
||||
if [ "$current_uid" != "${ARGUS_BUILD_UID}" ] && ! getent passwd "${ARGUS_BUILD_UID}" >/dev/null; then \
|
||||
usermod -u "${ARGUS_BUILD_UID}" web_proxy; \
|
||||
fi; \
|
||||
usermod -g "${ARGUS_BUILD_GID}" web_proxy || true; \
|
||||
else \
|
||||
if ! getent passwd "${ARGUS_BUILD_UID}" >/dev/null; then \
|
||||
useradd -M -s /usr/sbin/nologin -u "${ARGUS_BUILD_UID}" -g "${ARGUS_BUILD_GID}" web_proxy; \
|
||||
else \
|
||||
echo "UID ${ARGUS_BUILD_UID} already exists; skip creating user 'web_proxy'"; \
|
||||
fi; \
|
||||
fi; \
|
||||
chown -R "${ARGUS_BUILD_UID}:${ARGUS_BUILD_GID}" ${FRONTEND_BASE_PATH} /private/argus/etc /usr/local/bin || true
|
||||
|
||||
# 配置内网 apt 源 (如果指定了内网选项)
|
||||
RUN if [ "$USE_INTRANET" = "true" ]; then \
|
||||
@@ -56,13 +66,16 @@ RUN mkdir -p /var/log/supervisor
|
||||
# 复制启动脚本
|
||||
COPY src/web/build_tools/proxy/start-proxy-supervised.sh /usr/local/bin/start-proxy-supervised.sh
|
||||
RUN chmod +x /usr/local/bin/start-proxy-supervised.sh
|
||||
COPY src/web/build_tools/proxy/start-proxy-retry.sh /usr/local/bin/start-proxy-retry.sh
|
||||
RUN chmod +x /usr/local/bin/start-proxy-retry.sh
|
||||
|
||||
# 复制 DNS 监控脚本
|
||||
COPY src/web/build_tools/proxy/dns-monitor.sh /usr/local/bin/dns-monitor.sh
|
||||
# 统一复用 bind 模块的 dns-monitor 脚本,保持行为一致
|
||||
COPY src/bind/build/dns-monitor.sh /usr/local/bin/dns-monitor.sh
|
||||
RUN chmod +x /usr/local/bin/dns-monitor.sh
|
||||
|
||||
# 暴露端口
|
||||
EXPOSE 80
|
||||
EXPOSE 80 8080 8081 8082 8083 8084 8085
|
||||
|
||||
# 保持 root 用户,由 supervisor 控制 user 切换
|
||||
USER root
|
||||
|
||||
@@ -3,7 +3,7 @@ docker pull ubuntu:24.04
|
||||
source src/web/tests/.env
|
||||
|
||||
docker build \
|
||||
--build-arg ARGUS_UID=${ARGUS_UID} \
|
||||
--build-arg ARGUS_GID=${ARGUS_GID} \
|
||||
--build-arg ARGUS_BUILD_UID=${ARGUS_BUILD_UID} \
|
||||
--build-arg ARGUS_BUILD_GID=${ARGUS_BUILD_GID} \
|
||||
-f src/web/build_tools/proxy/Dockerfile -t argus-web-proxy:latest .
|
||||
docker save -o argus-web-proxy-latest.tar argus-web-proxy:latest
|
||||
|
||||
@@ -1,9 +0,0 @@
|
||||
server {
|
||||
listen 80;
|
||||
server_name alertmanager.alert.argus.com;
|
||||
|
||||
location / {
|
||||
set $alert_backend http://alertmanager.alert.argus.com:9093;
|
||||
proxy_pass $alert_backend;
|
||||
}
|
||||
}
|
||||
@@ -1,21 +0,0 @@
|
||||
# Elasticsearch
|
||||
server {
|
||||
listen 80;
|
||||
server_name es.log.argus.com;
|
||||
|
||||
location / {
|
||||
set $es_backend http://es.log.argus.com:9200;
|
||||
proxy_pass $es_backend;
|
||||
}
|
||||
}
|
||||
|
||||
# Kibana
|
||||
server {
|
||||
listen 80;
|
||||
server_name kibana.log.argus.com;
|
||||
|
||||
location / {
|
||||
set $kibana_backend http://kibana.log.argus.com:5601;
|
||||
proxy_pass $kibana_backend;
|
||||
}
|
||||
}
|
||||
@@ -1,27 +0,0 @@
|
||||
server {
|
||||
listen 80;
|
||||
server_name master.argus.com;
|
||||
|
||||
location / {
|
||||
set $master_backend http://master.argus.com:3000;
|
||||
proxy_pass $master_backend;
|
||||
proxy_set_header Host $host;
|
||||
proxy_set_header X-Real-IP $remote_addr;
|
||||
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
|
||||
proxy_set_header X-Forwarded-Proto $scheme;
|
||||
|
||||
# CORS 支持
|
||||
add_header 'Access-Control-Allow-Origin' 'http://web.argus.com' always;
|
||||
add_header 'Access-Control-Allow-Methods' 'GET, POST, PUT, DELETE, OPTIONS' always;
|
||||
add_header 'Access-Control-Allow-Headers' 'Origin, Content-Type, Accept, Authorization' always;
|
||||
|
||||
if ($request_method = OPTIONS) {
|
||||
add_header 'Access-Control-Allow-Origin' 'http://web.argus.com' always;
|
||||
add_header 'Access-Control-Allow-Methods' 'GET, POST, PUT, DELETE, OPTIONS' always;
|
||||
add_header 'Access-Control-Allow-Headers' 'Origin, Content-Type, Accept, Authorization' always;
|
||||
add_header 'Content-Length' 0;
|
||||
add_header 'Content-Type' 'text/plain';
|
||||
return 204;
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -1,21 +0,0 @@
|
||||
# Prometheus
|
||||
server {
|
||||
listen 80;
|
||||
server_name prometheus.metric.argus.com;
|
||||
|
||||
location / {
|
||||
set $prom_backend http://prom.metric.argus.com:9090;
|
||||
proxy_pass $prom_backend;
|
||||
}
|
||||
}
|
||||
|
||||
# Grafana
|
||||
server {
|
||||
listen 80;
|
||||
server_name grafana.metric.argus.com;
|
||||
|
||||
location / {
|
||||
set $grafana_backend http://grafana.metric.argus.com:3000;
|
||||
proxy_pass $grafana_backend;
|
||||
}
|
||||
}
|
||||
95
src/web/build_tools/proxy/conf.d/ports.conf
Normal file
95
src/web/build_tools/proxy/conf.d/ports.conf
Normal file
@@ -0,0 +1,95 @@
|
||||
map $http_upgrade $connection_upgrade { default upgrade; "" close; }
|
||||
|
||||
# 允许的跨域来源(仅用于 8084/8085)
|
||||
# 放开为任意来源:将来端口/域名变更均无需调整。
|
||||
# 注意:若前端需要携带凭证(cookies/Authorization),这种“回显 Origin”的方式比 "*" 更通用。
|
||||
map $http_origin $cors_allow {
|
||||
default $http_origin;
|
||||
}
|
||||
|
||||
# 8080 - Portal
|
||||
server {
|
||||
listen 8080;
|
||||
server_name _;
|
||||
proxy_set_header Host $host;
|
||||
proxy_set_header X-Real-IP $remote_addr;
|
||||
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
|
||||
proxy_set_header X-Forwarded-Proto $scheme;
|
||||
proxy_set_header Upgrade $http_upgrade;
|
||||
proxy_set_header Connection $connection_upgrade;
|
||||
proxy_http_version 1.1;
|
||||
location / { proxy_pass http://web.argus.com:8080/; }
|
||||
}
|
||||
|
||||
# 8081 - Grafana
|
||||
server {
|
||||
listen 8081;
|
||||
server_name _;
|
||||
proxy_set_header Host $host;
|
||||
proxy_set_header X-Real-IP $remote_addr;
|
||||
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
|
||||
proxy_set_header X-Forwarded-Proto $scheme;
|
||||
proxy_set_header Upgrade $http_upgrade;
|
||||
proxy_set_header Connection $connection_upgrade;
|
||||
proxy_http_version 1.1;
|
||||
location / { proxy_pass http://grafana.metric.argus.com:3000/; }
|
||||
}
|
||||
|
||||
# 8082 - Prometheus
|
||||
server {
|
||||
listen 8082;
|
||||
server_name _;
|
||||
proxy_set_header Host $host;
|
||||
proxy_set_header X-Real-IP $remote_addr;
|
||||
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
|
||||
proxy_set_header X-Forwarded-Proto $scheme;
|
||||
proxy_http_version 1.1;
|
||||
location / { proxy_pass http://prom.metric.argus.com:9090/; }
|
||||
}
|
||||
|
||||
# 8083 - Kibana
|
||||
server {
|
||||
listen 8083;
|
||||
server_name _;
|
||||
proxy_set_header Host $host;
|
||||
proxy_set_header X-Real-IP $remote_addr;
|
||||
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
|
||||
proxy_set_header X-Forwarded-Proto $scheme;
|
||||
proxy_set_header Upgrade $http_upgrade;
|
||||
proxy_set_header Connection $connection_upgrade;
|
||||
proxy_http_version 1.1;
|
||||
location / { proxy_pass http://kibana.log.argus.com:5601/; }
|
||||
}
|
||||
|
||||
# 8084 - Alertmanager(含 CORS)
|
||||
server {
|
||||
listen 8084;
|
||||
server_name _;
|
||||
proxy_set_header Host $host;
|
||||
proxy_set_header X-Real-IP $remote_addr;
|
||||
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
|
||||
proxy_set_header X-Forwarded-Proto $scheme;
|
||||
proxy_hide_header Access-Control-Allow-Origin;
|
||||
add_header 'Access-Control-Allow-Origin' $cors_allow always;
|
||||
add_header 'Access-Control-Allow-Methods' 'GET, POST, PUT, DELETE, OPTIONS' always;
|
||||
add_header 'Access-Control-Allow-Headers' 'Origin, Content-Type, Accept, Authorization' always;
|
||||
if ($request_method = OPTIONS) { return 204; }
|
||||
proxy_http_version 1.1;
|
||||
location / { proxy_pass http://alertmanager.alert.argus.com:9093/; }
|
||||
}
|
||||
|
||||
# 8085 - Master(新增,含 CORS)
|
||||
server {
|
||||
listen 8085;
|
||||
server_name _;
|
||||
proxy_set_header Host $host;
|
||||
proxy_set_header X-Real-IP $remote_addr;
|
||||
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
|
||||
proxy_set_header X-Forwarded-Proto $scheme;
|
||||
add_header 'Access-Control-Allow-Origin' $cors_allow always;
|
||||
add_header 'Access-Control-Allow-Methods' 'GET, POST, PUT, DELETE, OPTIONS' always;
|
||||
add_header 'Access-Control-Allow-Headers' 'Origin, Content-Type, Accept, Authorization' always;
|
||||
if ($request_method = OPTIONS) { return 204; }
|
||||
proxy_http_version 1.1;
|
||||
location / { proxy_pass http://master.argus.com:3000/; }
|
||||
}
|
||||
@@ -1,9 +0,0 @@
|
||||
server {
|
||||
listen 80;
|
||||
server_name web.argus.com;
|
||||
|
||||
location / {
|
||||
set $web_backend http://web.argus.com:8080;
|
||||
proxy_pass $web_backend;
|
||||
}
|
||||
}
|
||||
@@ -1,68 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
# DNS监控脚本 - 每10秒检查dns.conf是否有变化
|
||||
# 如果有变化则执行update-dns.sh脚本
|
||||
|
||||
DNS_CONF="/private/argus/etc/dns.conf"
|
||||
DNS_BACKUP="/tmp/dns.conf.backup"
|
||||
UPDATE_SCRIPT="/private/argus/etc/update-dns.sh"
|
||||
LOG_FILE="/var/log/supervisor/dns-monitor.log"
|
||||
|
||||
# 确保日志文件存在
|
||||
touch "$LOG_FILE"
|
||||
|
||||
log_message() {
|
||||
echo "$(date '+%Y-%m-%d %H:%M:%S') [DNS-Monitor] $1" >> "$LOG_FILE"
|
||||
}
|
||||
|
||||
log_message "DNS监控脚本启动"
|
||||
|
||||
while true; do
|
||||
if [ -f "$DNS_CONF" ]; then
|
||||
if [ -f "$DNS_BACKUP" ]; then
|
||||
# 比较文件内容
|
||||
if ! cmp -s "$DNS_CONF" "$DNS_BACKUP"; then
|
||||
log_message "检测到DNS配置变化"
|
||||
|
||||
# 更新备份文件
|
||||
cp "$DNS_CONF" "$DNS_BACKUP"
|
||||
|
||||
# 执行更新脚本
|
||||
if [ -x "$UPDATE_SCRIPT" ]; then
|
||||
log_message "执行DNS更新脚本: $UPDATE_SCRIPT"
|
||||
"$UPDATE_SCRIPT" >> "$LOG_FILE" 2>&1
|
||||
if [ $? -eq 0 ]; then
|
||||
log_message "DNS更新脚本执行成功"
|
||||
else
|
||||
log_message "DNS更新脚本执行失败"
|
||||
fi
|
||||
else
|
||||
log_message "警告: 更新脚本不存在或不可执行: $UPDATE_SCRIPT"
|
||||
fi
|
||||
fi
|
||||
else
|
||||
|
||||
# 第一次检测到配置文件,执行更新脚本
|
||||
if [ -x "$UPDATE_SCRIPT" ]; then
|
||||
log_message "执行DNS更新脚本: $UPDATE_SCRIPT"
|
||||
"$UPDATE_SCRIPT" >> "$LOG_FILE" 2>&1
|
||||
if [ $? -eq 0 ]; then
|
||||
log_message "DNS更新脚本执行成功"
|
||||
|
||||
# 第一次运行,创建备份并执行更新
|
||||
cp "$DNS_CONF" "$DNS_BACKUP"
|
||||
log_message "创建DNS配置备份文件"
|
||||
|
||||
else
|
||||
log_message "DNS更新脚本执行失败"
|
||||
fi
|
||||
else
|
||||
log_message "警告: 更新脚本不存在或不可执行: $UPDATE_SCRIPT"
|
||||
fi
|
||||
fi
|
||||
else
|
||||
log_message "警告: DNS配置文件不存在: $DNS_CONF"
|
||||
fi
|
||||
|
||||
sleep 10
|
||||
done
|
||||
@@ -1,4 +1,4 @@
|
||||
user web_proxy;
|
||||
user root;
|
||||
worker_processes auto;
|
||||
|
||||
events {
|
||||
@@ -13,6 +13,7 @@ http {
|
||||
|
||||
# 使用系统 resolv.conf(由 update-dns.sh 动态更新)
|
||||
resolver __RESOLVERS__ valid=30s ipv6=off;
|
||||
resolver_timeout 5s;
|
||||
|
||||
# 启用访问日志
|
||||
access_log /var/log/nginx/access.log;
|
||||
|
||||
20
src/web/build_tools/proxy/start-proxy-retry.sh
Normal file
20
src/web/build_tools/proxy/start-proxy-retry.sh
Normal file
@@ -0,0 +1,20 @@
|
||||
#!/bin/sh
|
||||
set -eu
|
||||
|
||||
MAX=${RETRY_MAX:-10}
|
||||
DELAY=${RETRY_DELAY:-10}
|
||||
ATTEMPT=1
|
||||
|
||||
echo "[INFO] proxy retry wrapper: max=${MAX}, delay=${DELAY}s"
|
||||
|
||||
while [ "$ATTEMPT" -le "$MAX" ]; do
|
||||
echo "[INFO] starting proxy attempt ${ATTEMPT}/${MAX}"
|
||||
/usr/local/bin/start-proxy-supervised.sh && exit 0 || true
|
||||
echo "[WARN] proxy exited (attempt ${ATTEMPT}/${MAX}); sleeping ${DELAY}s before retry"
|
||||
sleep "$DELAY"
|
||||
ATTEMPT=$((ATTEMPT+1))
|
||||
done
|
||||
|
||||
echo "[ERROR] proxy failed after ${MAX} attempts"
|
||||
exit 1
|
||||
|
||||
@@ -9,8 +9,8 @@ DNS_CONF_PRIVATE="/private/argus/etc/dns.conf"
|
||||
DNS_CONF_SYSTEM="/etc/resolv.conf"
|
||||
DNS_DIR="/private/argus/etc"
|
||||
DNS_SCRIPT="${DNS_DIR}/update-dns.sh"
|
||||
RUNTIME_UID="${ARGUS_UID:-2133}"
|
||||
RUNTIME_GID="${ARGUS_GID:-2015}"
|
||||
RUNTIME_UID="${ARGUS_BUILD_UID:-2133}"
|
||||
RUNTIME_GID="${ARGUS_BUILD_GID:-2015}"
|
||||
|
||||
mkdir -p "$DNS_DIR"
|
||||
chown -R "$RUNTIME_UID:$RUNTIME_GID" "$DNS_DIR" 2>/dev/null || true
|
||||
@@ -46,6 +46,10 @@ echo "检测到 DNS 服务器列表: $RESOLVERS"
|
||||
# ========== 生成 nginx.conf ==========
|
||||
if [ -f "$TEMPLATE" ]; then
|
||||
echo "从模板生成 nginx.conf ..."
|
||||
# 合并 Docker 内置 DNS 以保障解析 Compose 服务名
|
||||
if ! echo " $RESOLVERS " | grep -q " 127.0.0.11 "; then
|
||||
RESOLVERS="127.0.0.11 ${RESOLVERS}"
|
||||
fi
|
||||
sed "s|__RESOLVERS__|$RESOLVERS|" "$TEMPLATE" > "$TARGET"
|
||||
else
|
||||
echo "错误: 找不到 nginx.conf.template ($TEMPLATE)"
|
||||
@@ -55,6 +59,33 @@ fi
|
||||
# 打印生成结果供排查
|
||||
grep resolver "$TARGET" || true
|
||||
|
||||
# ========== 等待上游域名准备(避免启动即解析失败) ==========
|
||||
UPSTREAM_DOMAINS=(
|
||||
web.argus.com
|
||||
grafana.metric.argus.com
|
||||
prom.metric.argus.com
|
||||
kibana.log.argus.com
|
||||
alertmanager.alert.argus.com
|
||||
master.argus.com
|
||||
)
|
||||
WAIT_MAX=15
|
||||
WAITED=0
|
||||
MISSING=()
|
||||
while :; do
|
||||
MISSING=()
|
||||
for d in "${UPSTREAM_DOMAINS[@]}"; do
|
||||
if [ ! -s "/private/argus/etc/${d}" ]; then
|
||||
MISSING+=("$d")
|
||||
fi
|
||||
done
|
||||
if [ ${#MISSING[@]} -eq 0 ] || [ "$WAITED" -ge "$WAIT_MAX" ]; then
|
||||
break
|
||||
fi
|
||||
echo "[INFO] 等待上游域名记录生成(${WAITED}/${WAIT_MAX}) 缺失: ${MISSING[*]}"
|
||||
sleep 1
|
||||
WAITED=$((WAITED+1))
|
||||
done
|
||||
|
||||
echo "[INFO] Launching nginx..."
|
||||
|
||||
# 启动 nginx 前台模式
|
||||
|
||||
@@ -5,12 +5,12 @@ pidfile=/var/run/supervisord.pid
|
||||
user=root
|
||||
|
||||
[program:proxy]
|
||||
command=/usr/local/bin/start-proxy-supervised.sh
|
||||
command=/usr/local/bin/start-proxy-retry.sh
|
||||
user=root
|
||||
stdout_logfile=/var/log/supervisor/web-proxy.log
|
||||
stderr_logfile=/var/log/supervisor/web-proxy_error.log
|
||||
autorestart=true
|
||||
startretries=3
|
||||
startretries=10
|
||||
startsecs=5
|
||||
stopwaitsecs=10
|
||||
killasgroup=true
|
||||
|
||||
@@ -8,6 +8,8 @@
|
||||
</head>
|
||||
<body>
|
||||
<div id="root"></div>
|
||||
<!-- Runtime-injected config: ports/host; generated by start-web-supervised.sh -->
|
||||
<script src="/argus-config.js"></script>
|
||||
<script type="module" src="/src/main.jsx"></script>
|
||||
</body>
|
||||
</html>
|
||||
|
||||
@@ -71,7 +71,7 @@ export function NodeTable({
|
||||
size="xs"
|
||||
variant="outline"
|
||||
component="a"
|
||||
href={`${EXTERNAL_HOST.GRAFANA}/d/node_gpu_metrics/node-and-gpu-metrics?var-hostname=${encodeURIComponent(node.name)}`}
|
||||
href={`${EXTERNAL_HOST.GRAFANA}/d/node_gpu_metrics_by_hostname/node-and-gpu-metrics-by-hostname?var-hostname=${encodeURIComponent(node.name)}`}
|
||||
target="_blank"
|
||||
rel="noopener noreferrer"
|
||||
>
|
||||
|
||||
@@ -1,30 +1,53 @@
|
||||
// config/api.js
|
||||
|
||||
// Master 节点相关 API
|
||||
// 运行时解析主机名,统一按端口访问多服务
|
||||
const HOST = (typeof window !== 'undefined' && (window.__ARGUS_PUBLIC_HOST__ || window.location.hostname)) || 'localhost';
|
||||
|
||||
// 默认端口常量(作为兜底值)
|
||||
const DEFAULT_PORTS = {
|
||||
MASTER: 8085, // 经网关(含 CORS)
|
||||
ALERTMANAGER: 8084,
|
||||
GRAFANA: 8081,
|
||||
PROMETHEUS: 8082,
|
||||
KIBANA: 8083,
|
||||
};
|
||||
|
||||
// 运行期注入:/argus-config.js 会在 window.__ARGUS_PORTS__ 写入外部端口
|
||||
const RUNTIME_PORTS = (typeof window !== 'undefined' && window.__ARGUS_PORTS__) || {};
|
||||
const PORTS = {
|
||||
MASTER: Number(RUNTIME_PORTS.MASTER) || DEFAULT_PORTS.MASTER,
|
||||
ALERTMANAGER: Number(RUNTIME_PORTS.ALERTMANAGER) || DEFAULT_PORTS.ALERTMANAGER,
|
||||
GRAFANA: Number(RUNTIME_PORTS.GRAFANA) || DEFAULT_PORTS.GRAFANA,
|
||||
PROMETHEUS: Number(RUNTIME_PORTS.PROMETHEUS) || DEFAULT_PORTS.PROMETHEUS,
|
||||
KIBANA: Number(RUNTIME_PORTS.KIBANA) || DEFAULT_PORTS.KIBANA,
|
||||
};
|
||||
|
||||
const BASE = {
|
||||
MASTER: `http://${HOST}:${PORTS.MASTER}`,
|
||||
ALERT: `http://${HOST}:${PORTS.ALERTMANAGER}`,
|
||||
GRAFANA: `http://${HOST}:${PORTS.GRAFANA}`,
|
||||
PROM: `http://${HOST}:${PORTS.PROMETHEUS}`,
|
||||
KIBANA: `http://${HOST}:${PORTS.KIBANA}`,
|
||||
};
|
||||
|
||||
// Master 节点相关 API(统一走 8085)
|
||||
export const MASTER_API = {
|
||||
// 节点列表
|
||||
LIST: "http://master.argus.com/api/v1/master/nodes",
|
||||
|
||||
// 节点详情(需要 nodeId)
|
||||
DETAIL: (nodeId) => `http://master.argus.com/api/v1/master/nodes/${nodeId}`,
|
||||
|
||||
// 节点配置(需要 nodeId)
|
||||
CONFIG: (nodeId) => `http://master.argus.com/api/v1/master/nodes/${nodeId}/config`,
|
||||
|
||||
// 节点统计信息
|
||||
STATISTICS: "http://master.argus.com/api/v1/master/nodes/statistics",
|
||||
LIST: `${BASE.MASTER}/api/v1/master/nodes`,
|
||||
DETAIL: (nodeId) => `${BASE.MASTER}/api/v1/master/nodes/${nodeId}`,
|
||||
CONFIG: (nodeId) => `${BASE.MASTER}/api/v1/master/nodes/${nodeId}/config`,
|
||||
STATISTICS: `${BASE.MASTER}/api/v1/master/nodes/statistics`,
|
||||
};
|
||||
|
||||
// 其他外部 API
|
||||
// 其他外部 API(8084)
|
||||
export const EXTERNAL_API = {
|
||||
ALERTS_INFOS: "http://alertmanager.alert.argus.com/api/v2/alerts",
|
||||
ALERTS_INFOS: `${BASE.ALERT}/api/v2/alerts`,
|
||||
};
|
||||
|
||||
// 外部服务 Host
|
||||
// 外部服务 Host(端口化)
|
||||
export const EXTERNAL_HOST = {
|
||||
ALERTS: "http://alertmanager.alert.argus.com",
|
||||
GRAFANA: "http://grafana.metric.argus.com",
|
||||
GRAFANA_DASHBOARD: "http://grafana.metric.argus.com/d/cluster-dashboard/cluster-dashboard",
|
||||
PROMETHEUS: "http://prometheus.metric.argus.com",
|
||||
KIBANA: "http://kibana.log.argus.com/app/discover",
|
||||
ALERTS: `${BASE.ALERT}`,
|
||||
GRAFANA: `${BASE.GRAFANA}`,
|
||||
GRAFANA_DASHBOARD: `${BASE.GRAFANA}/d/cluster-dashboard/cluster-dashboard`,
|
||||
PROMETHEUS: `${BASE.PROM}`,
|
||||
KIBANA: `${BASE.KIBANA}/app/discover`,
|
||||
};
|
||||
|
||||
@@ -4,15 +4,15 @@ services:
|
||||
context: ../../../
|
||||
dockerfile: src/web/build_tools/frontend/Dockerfile
|
||||
args:
|
||||
ARGUS_UID: ${ARGUS_UID:-2133}
|
||||
ARGUS_GID: ${ARGUS_GID:-2015}
|
||||
ARGUS_BUILD_UID: ${ARGUS_BUILD_UID:-2133}
|
||||
ARGUS_BUILD_GID: ${ARGUS_BUILD_GID:-2015}
|
||||
USE_INTRANET: ${USE_INTRANET:-false}
|
||||
image: argus-web-frontend:latest
|
||||
container_name: argus-web-frontend
|
||||
environment:
|
||||
- ALERTMANAGER_BASE_PATH=/private/argus/web/frontend
|
||||
- ARGUS_UID=${ARGUS_UID:-2133}
|
||||
- ARGUS_GID=${ARGUS_GID:-2015}
|
||||
- ARGUS_BUILD_UID=${ARGUS_BUILD_UID:-2133}
|
||||
- ARGUS_BUILD_GID=${ARGUS_BUILD_GID:-2015}
|
||||
ports:
|
||||
- "${ARGUS_WEB_PORT:-8080}:80"
|
||||
volumes:
|
||||
@@ -31,14 +31,14 @@ services:
|
||||
context: ../../../
|
||||
dockerfile: src/web/build_tools/proxy/Dockerfile
|
||||
args:
|
||||
ARGUS_UID: ${ARGUS_UID:-2133}
|
||||
ARGUS_GID: ${ARGUS_GID:-2015}
|
||||
ARGUS_BUILD_UID: ${ARGUS_BUILD_UID:-2133}
|
||||
ARGUS_BUILD_GID: ${ARGUS_BUILD_GID:-2015}
|
||||
USE_INTRANET: ${USE_INTRANET:-false}
|
||||
image: argus-web-proxy:latest
|
||||
container_name: argus-web-proxy
|
||||
environment:
|
||||
- ARGUS_UID=${ARGUS_UID:-2133}
|
||||
- ARGUS_GID=${ARGUS_GID:-2015}
|
||||
- ARGUS_BUILD_UID=${ARGUS_BUILD_UID:-2133}
|
||||
- ARGUS_BUILD_GID=${ARGUS_BUILD_GID:-2015}
|
||||
ports:
|
||||
- "8088:80"
|
||||
volumes:
|
||||
|
||||
Reference in New Issue
Block a user