完成a6000测试系统构建、部署、测试整合 (#35)
测试方案: - lm2机器端口映射到本机:18080, 18081, 8082-8085 - 访问URL: http://localhost:18080/dashboard 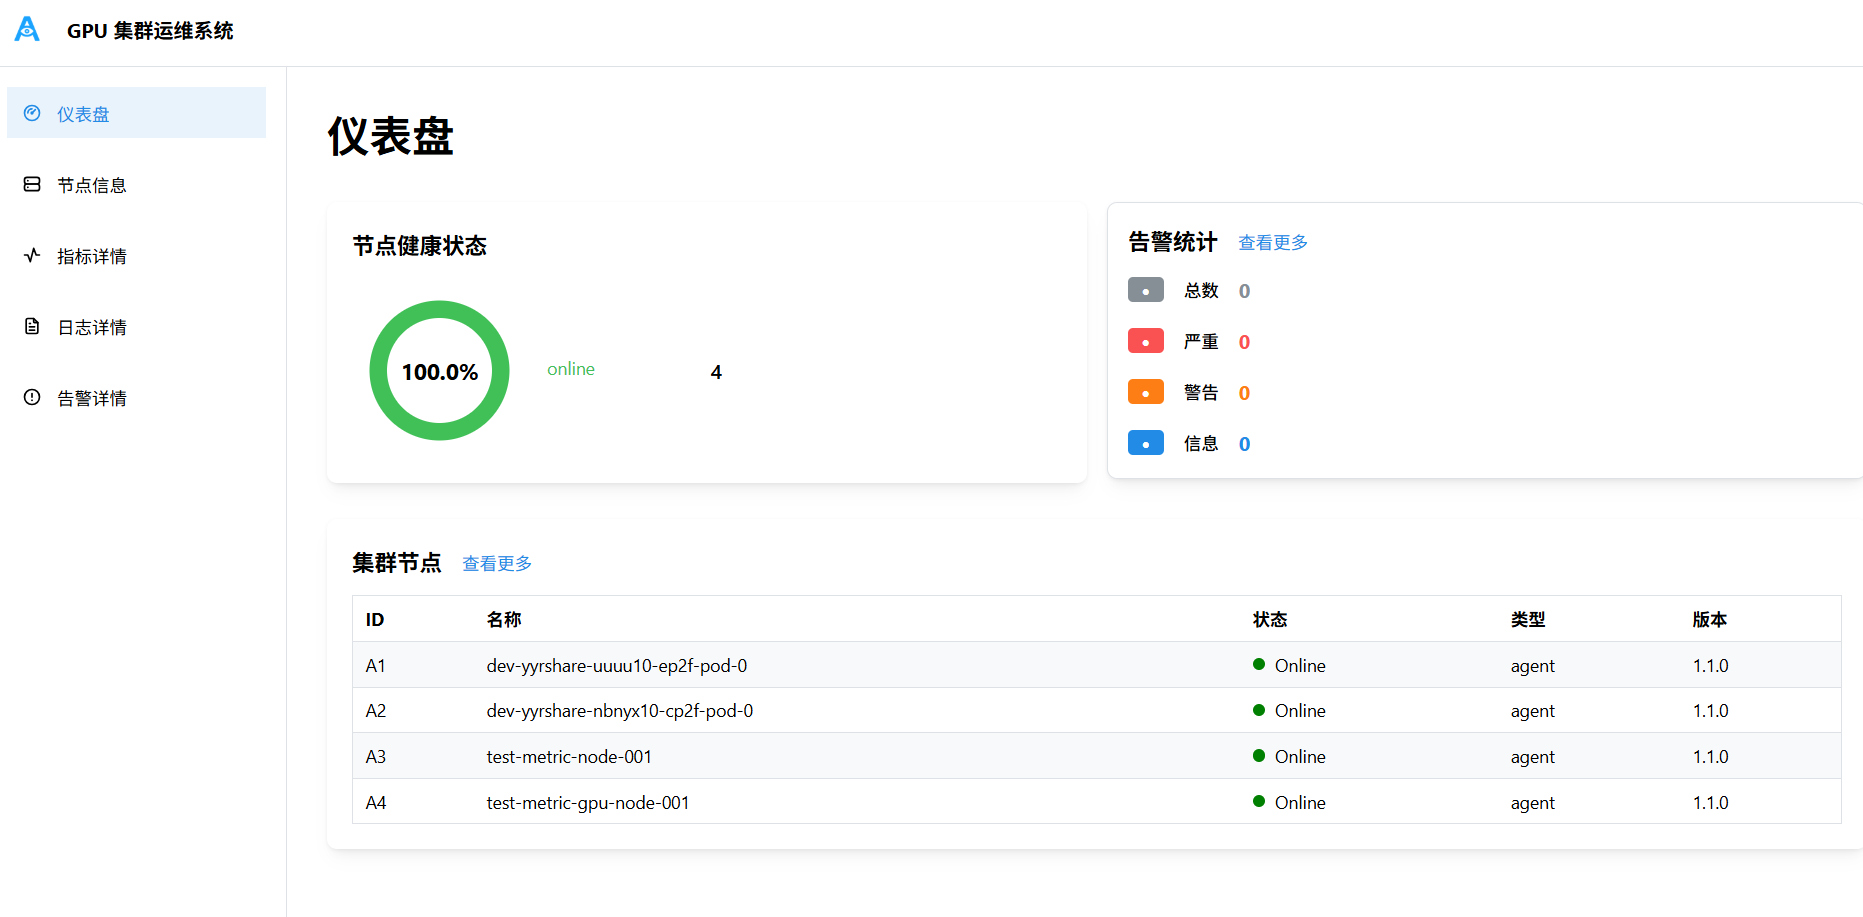 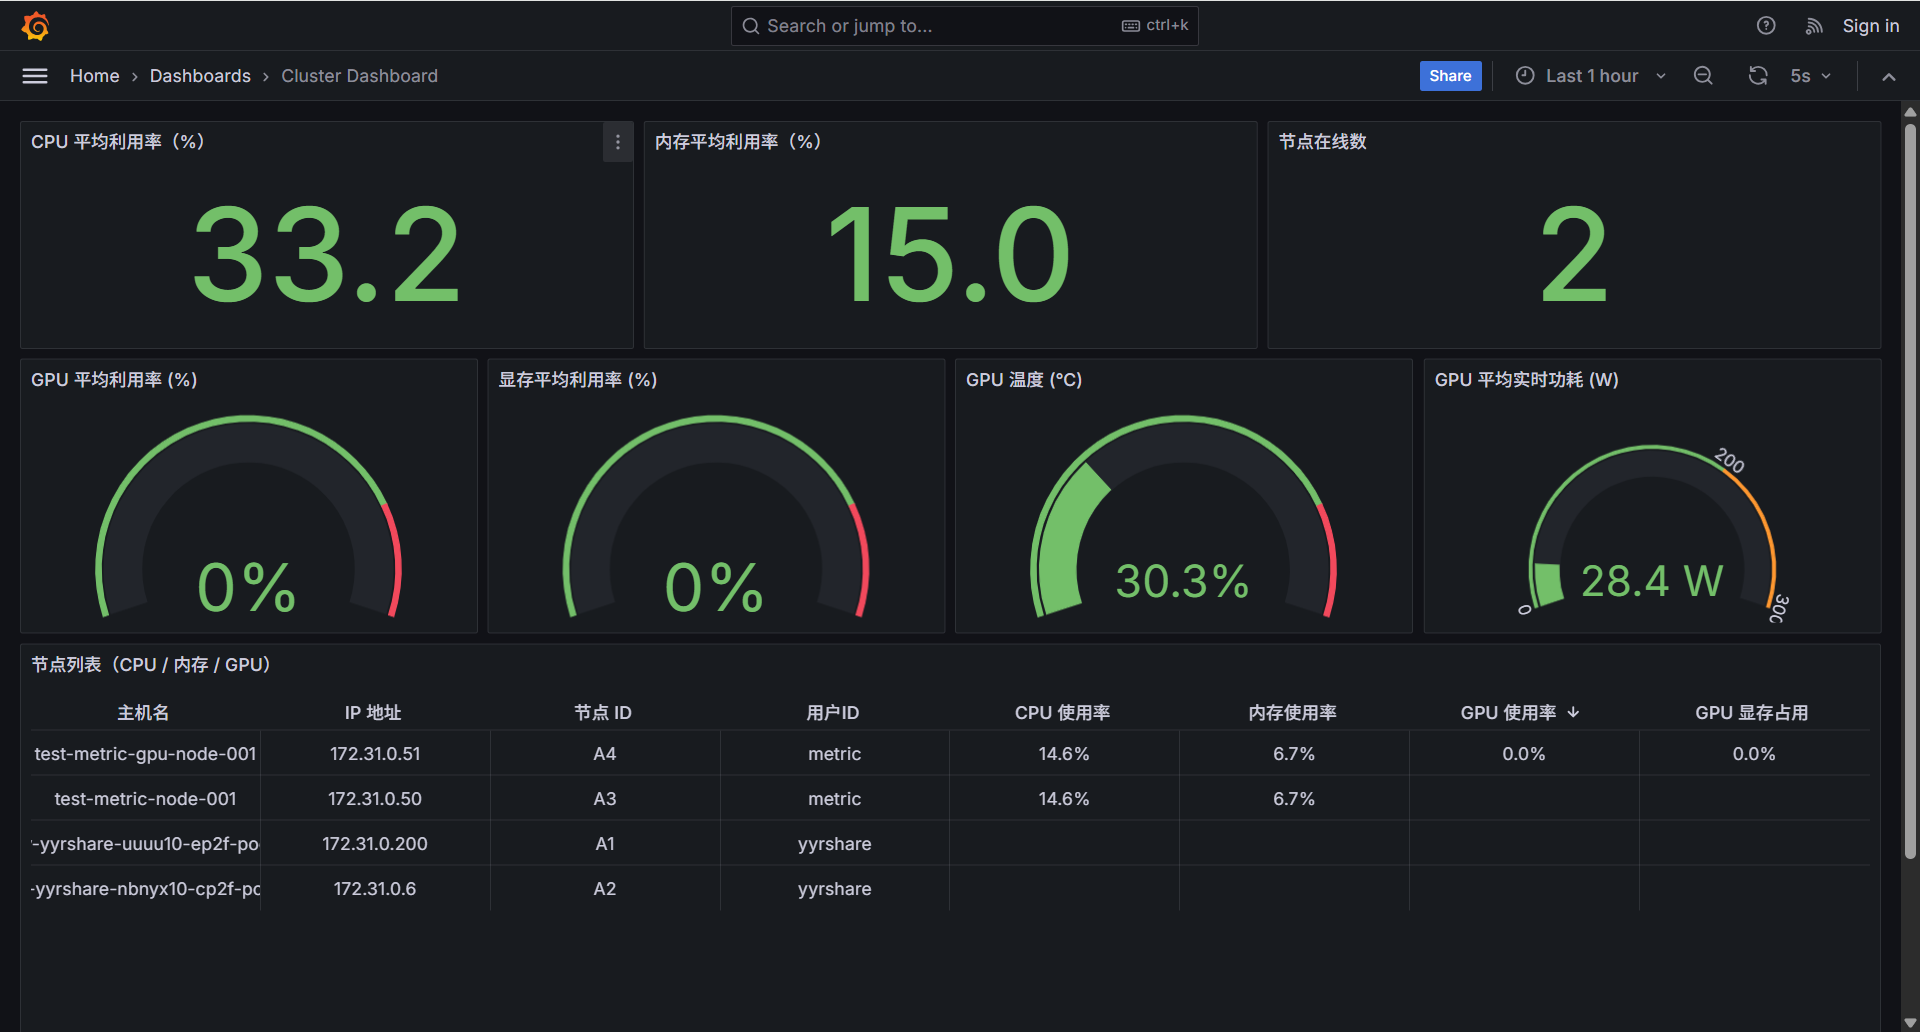 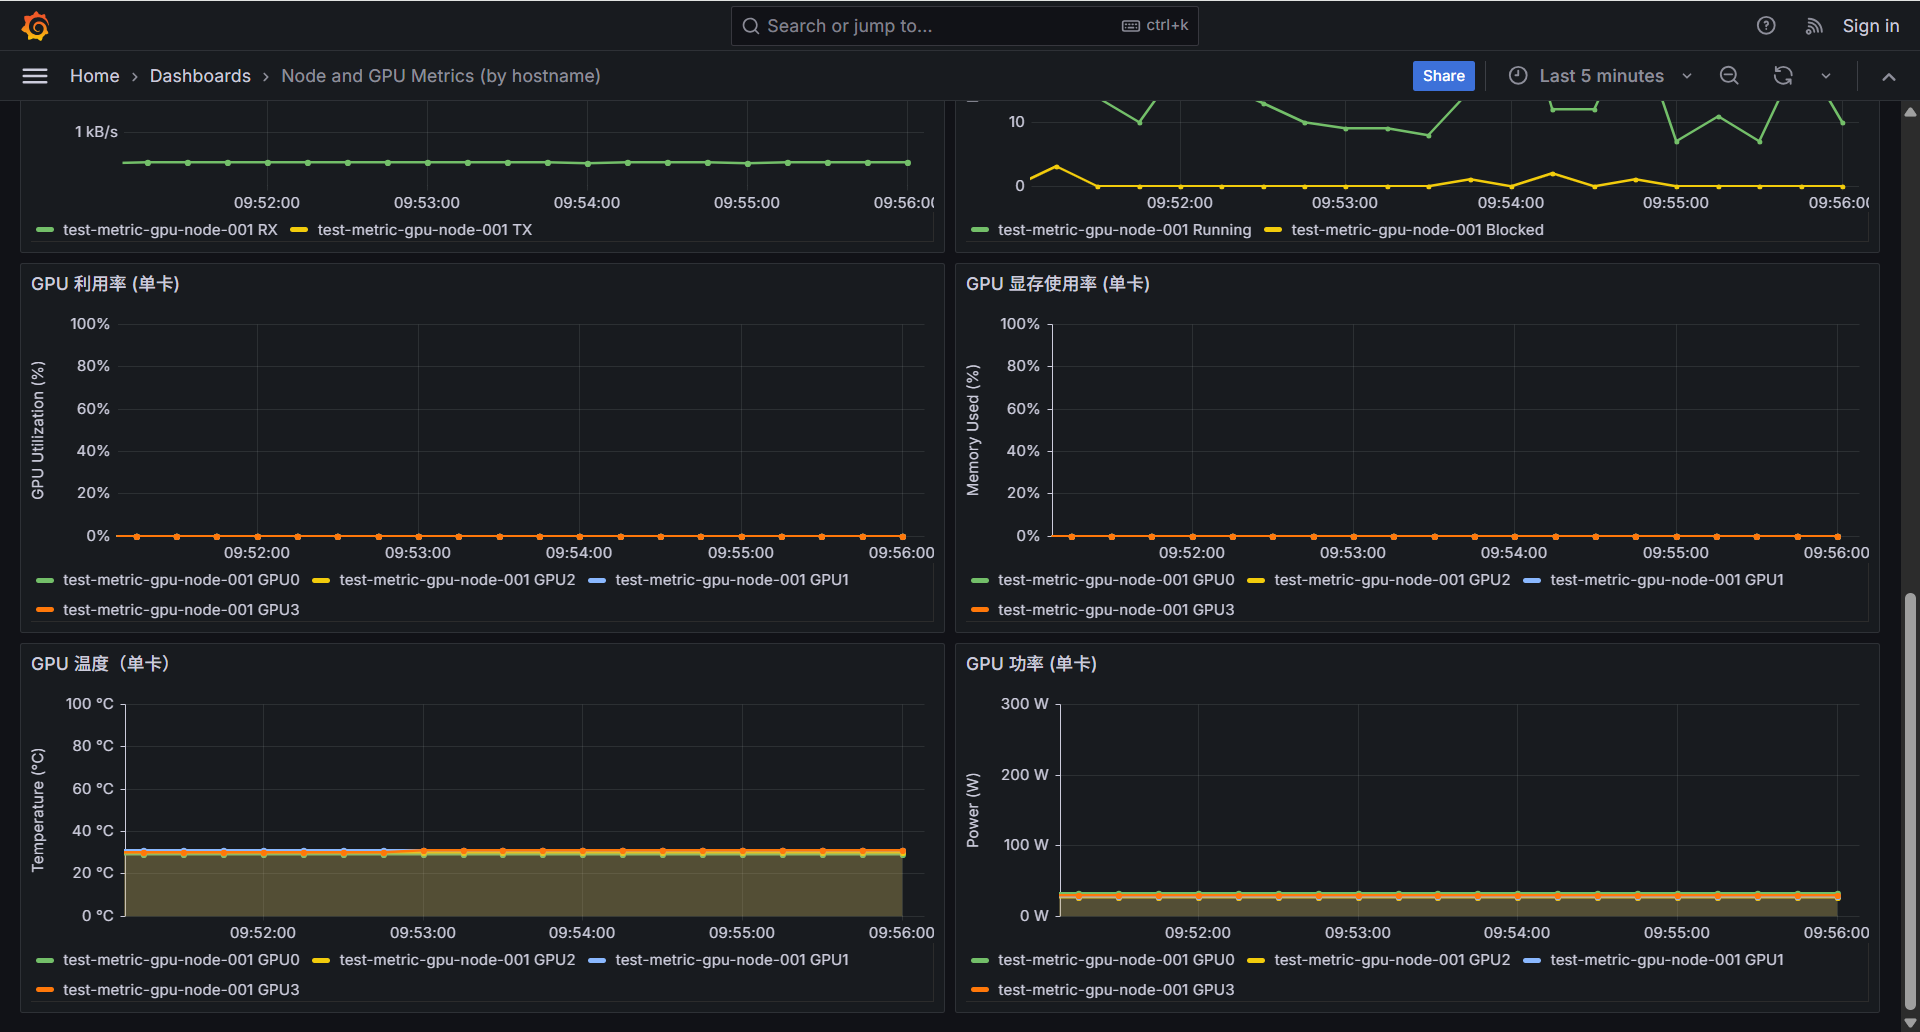 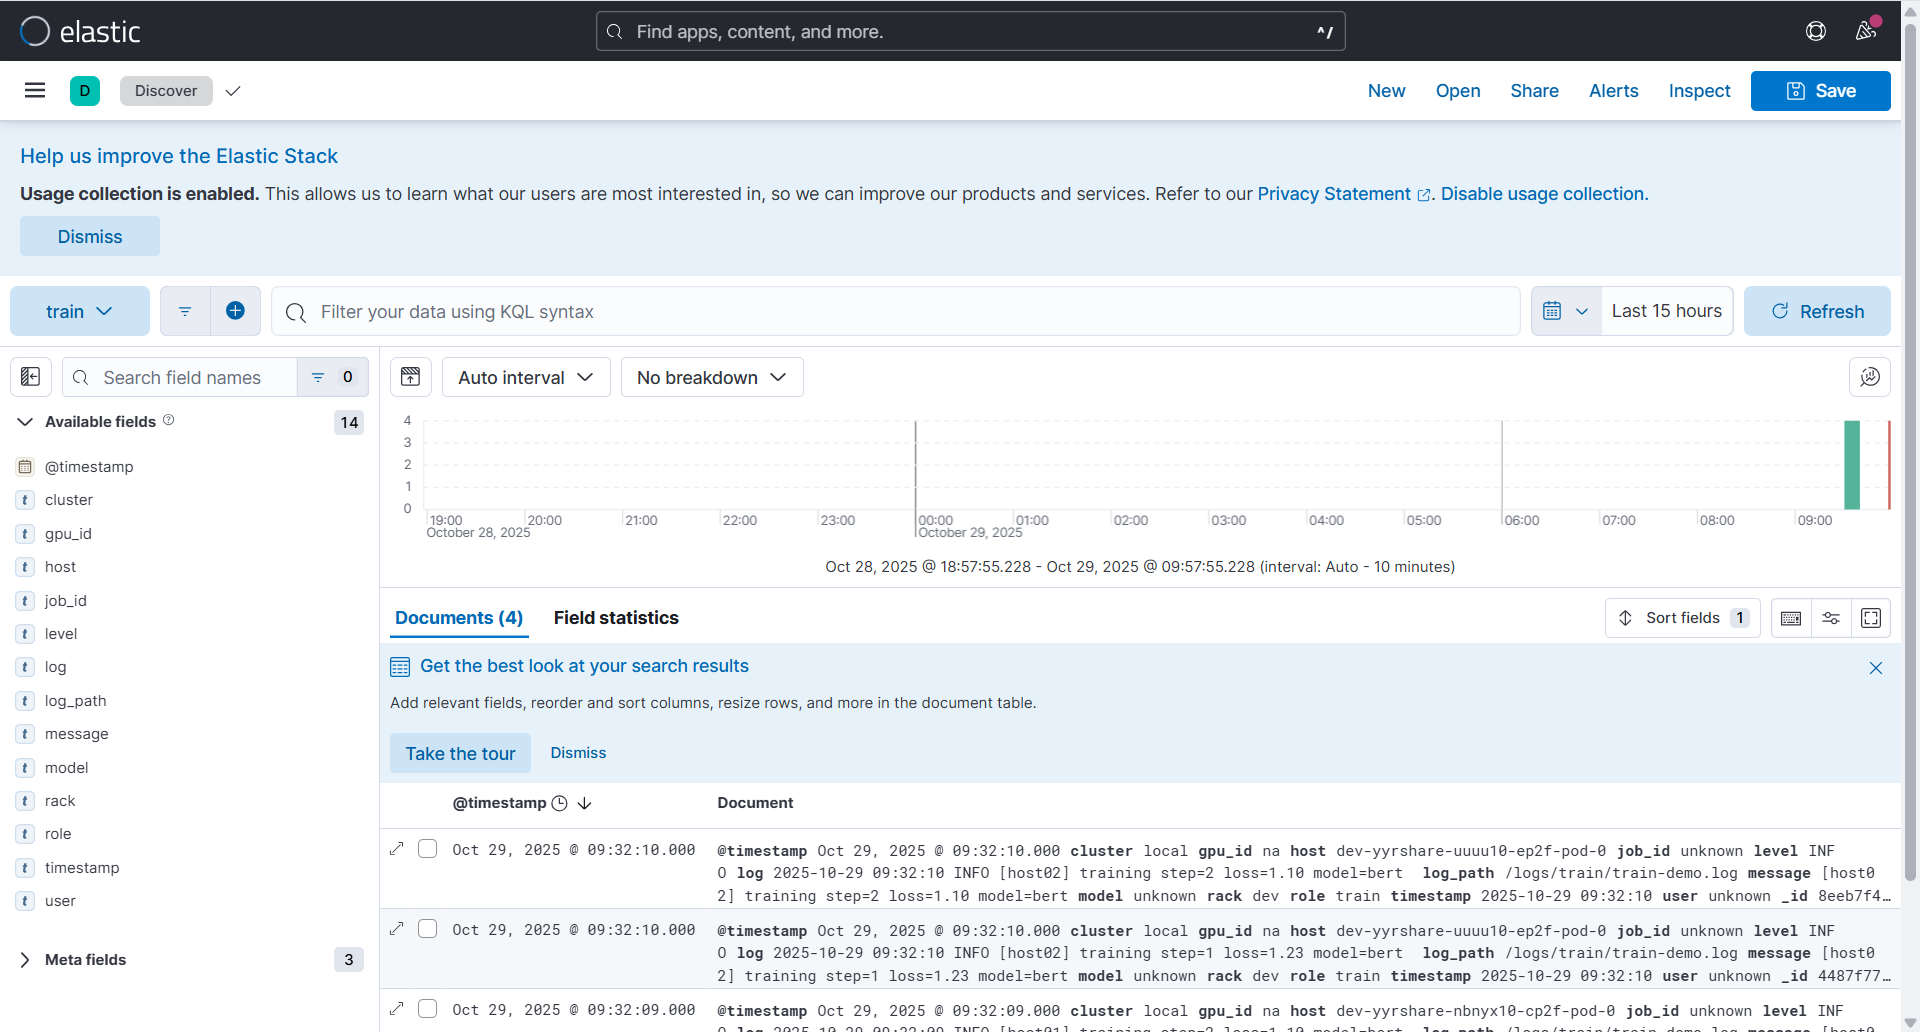 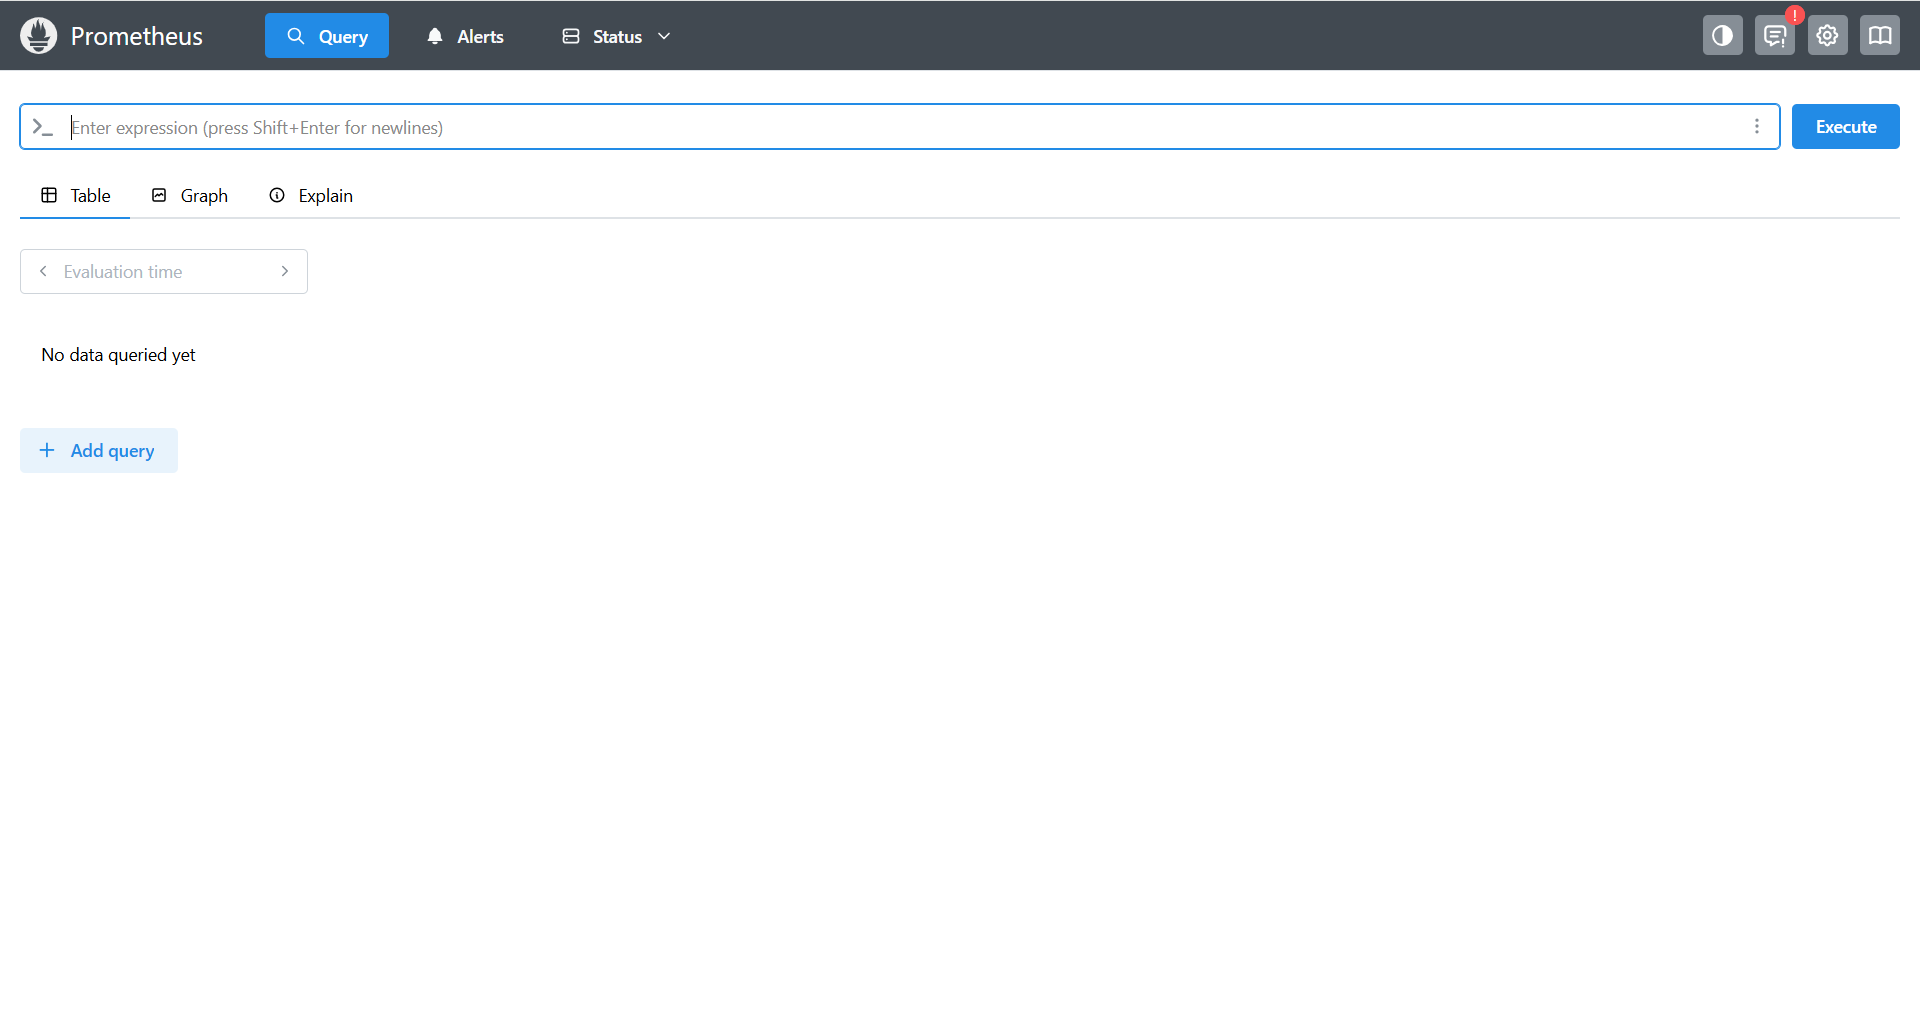  端到端测试通过: 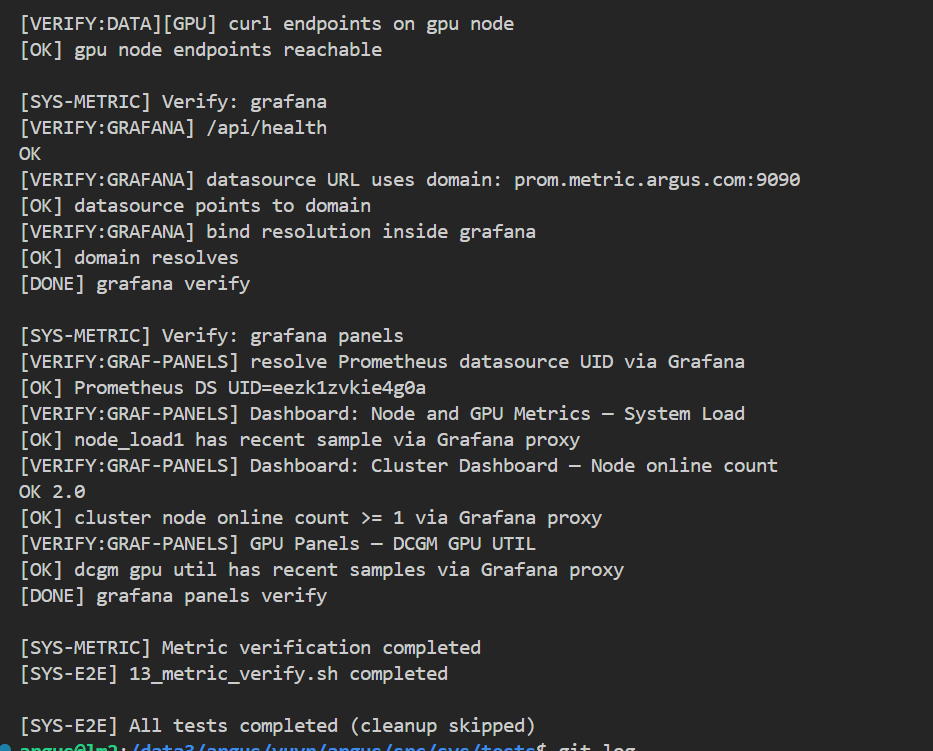 Co-authored-by: sundapeng.sdp <sundapeng@hashdata.cn> Reviewed-on: #35 Reviewed-by: xuxt <xuxt@zgclab.edu.cn> Reviewed-by: sundapeng <sundp@mail.zgclab.edu.cn> Reviewed-by: huhy <husteryezi@163.com>
This commit was merged in pull request #35.
This commit is contained in:

@@ -11,13 +11,6 @@ RUN if [ "$USE_INTRANET" = "true" ]; then \
|
||||
echo "deb [trusted=yes] http://10.68.64.1/ubuntu2204/ jammy main" > /etc/apt/sources.list && \
|
||||
echo 'Acquire::https::Verify-Peer "false";' > /etc/apt/apt.conf.d/99disable-ssl-check && \
|
||||
echo 'Acquire::https::Verify-Host "false";' >> /etc/apt/apt.conf.d/99disable-ssl-check; \
|
||||
else \
|
||||
echo "Configuring fast apt sources for external network..." && \
|
||||
find /etc/apt -name "sources.list*" -exec sed -i 's/archive.ubuntu.com/mirrors.aliyun.com/g' {} \; && \
|
||||
find /etc/apt -name "sources.list*" -exec sed -i 's/security.ubuntu.com/mirrors.aliyun.com/g' {} \; && \
|
||||
echo "deb http://mirrors.aliyun.com/ubuntu/ jammy main restricted universe multiverse" > /etc/apt/sources.list && \
|
||||
echo "deb http://mirrors.aliyun.com/ubuntu/ jammy-updates main restricted universe multiverse" >> /etc/apt/sources.list && \
|
||||
echo "deb http://mirrors.aliyun.com/ubuntu/ jammy-security main restricted universe multiverse" >> /etc/apt/sources.list; \
|
||||
fi
|
||||
|
||||
# 验证源配置并安装常用工具
|
||||
@@ -61,10 +54,25 @@ RUN mkdir -p ${PROMETHEUS_BASE_PATH}/rules \
|
||||
&& ln -s ${PROMETHEUS_BASE_PATH} /prometheus
|
||||
|
||||
# 修改 Prometheus 用户 UID/GID 并授权
|
||||
RUN usermod -u ${ARGUS_BUILD_UID} nobody && \
|
||||
groupmod -g ${ARGUS_BUILD_GID} nogroup && \
|
||||
chown -h nobody:nogroup /prometheus && \
|
||||
chown -R nobody:nogroup ${PROMETHEUS_BASE_PATH} && \
|
||||
RUN set -eux; \
|
||||
existing_user=""; \
|
||||
if getent passwd "${ARGUS_BUILD_UID}" >/dev/null 2>&1; then \
|
||||
existing_user="$(getent passwd "${ARGUS_BUILD_UID}" | cut -d: -f1)"; \
|
||||
fi; \
|
||||
if [ -n "$existing_user" ] && [ "$existing_user" != "nobody" ]; then \
|
||||
userdel -r "$existing_user" || true; \
|
||||
fi; \
|
||||
existing_group=""; \
|
||||
if getent group "${ARGUS_BUILD_GID}" >/dev/null 2>&1; then \
|
||||
existing_group="$(getent group "${ARGUS_BUILD_GID}" | cut -d: -f1)"; \
|
||||
fi; \
|
||||
if [ -n "$existing_group" ] && [ "$existing_group" != "nogroup" ]; then \
|
||||
groupdel "$existing_group" || true; \
|
||||
fi; \
|
||||
usermod -u ${ARGUS_BUILD_UID} nobody; \
|
||||
groupmod -g ${ARGUS_BUILD_GID} nogroup; \
|
||||
chown -h nobody:nogroup /prometheus; \
|
||||
chown -R nobody:nogroup ${PROMETHEUS_BASE_PATH}; \
|
||||
chown -R nobody:nogroup /etc/prometheus
|
||||
|
||||
# supervisor 配置
|
||||
|
||||
Reference in New Issue
Block a user